Wednesday, July 29, 2026 · generated · about 4 min read
Morning Brief
Patch today vendors with the most new CVEs today
- Apache 8 critical 45
- WordPress 5 critical 39
- IBM 5 critical 31
- Xen 18
- Three Learning 5 critical 15
- Unknown 6 critical 12
- koxudaxi 12
- HashiCorp 4 critical 11
- Adobe 10
- Red Hat 7
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-
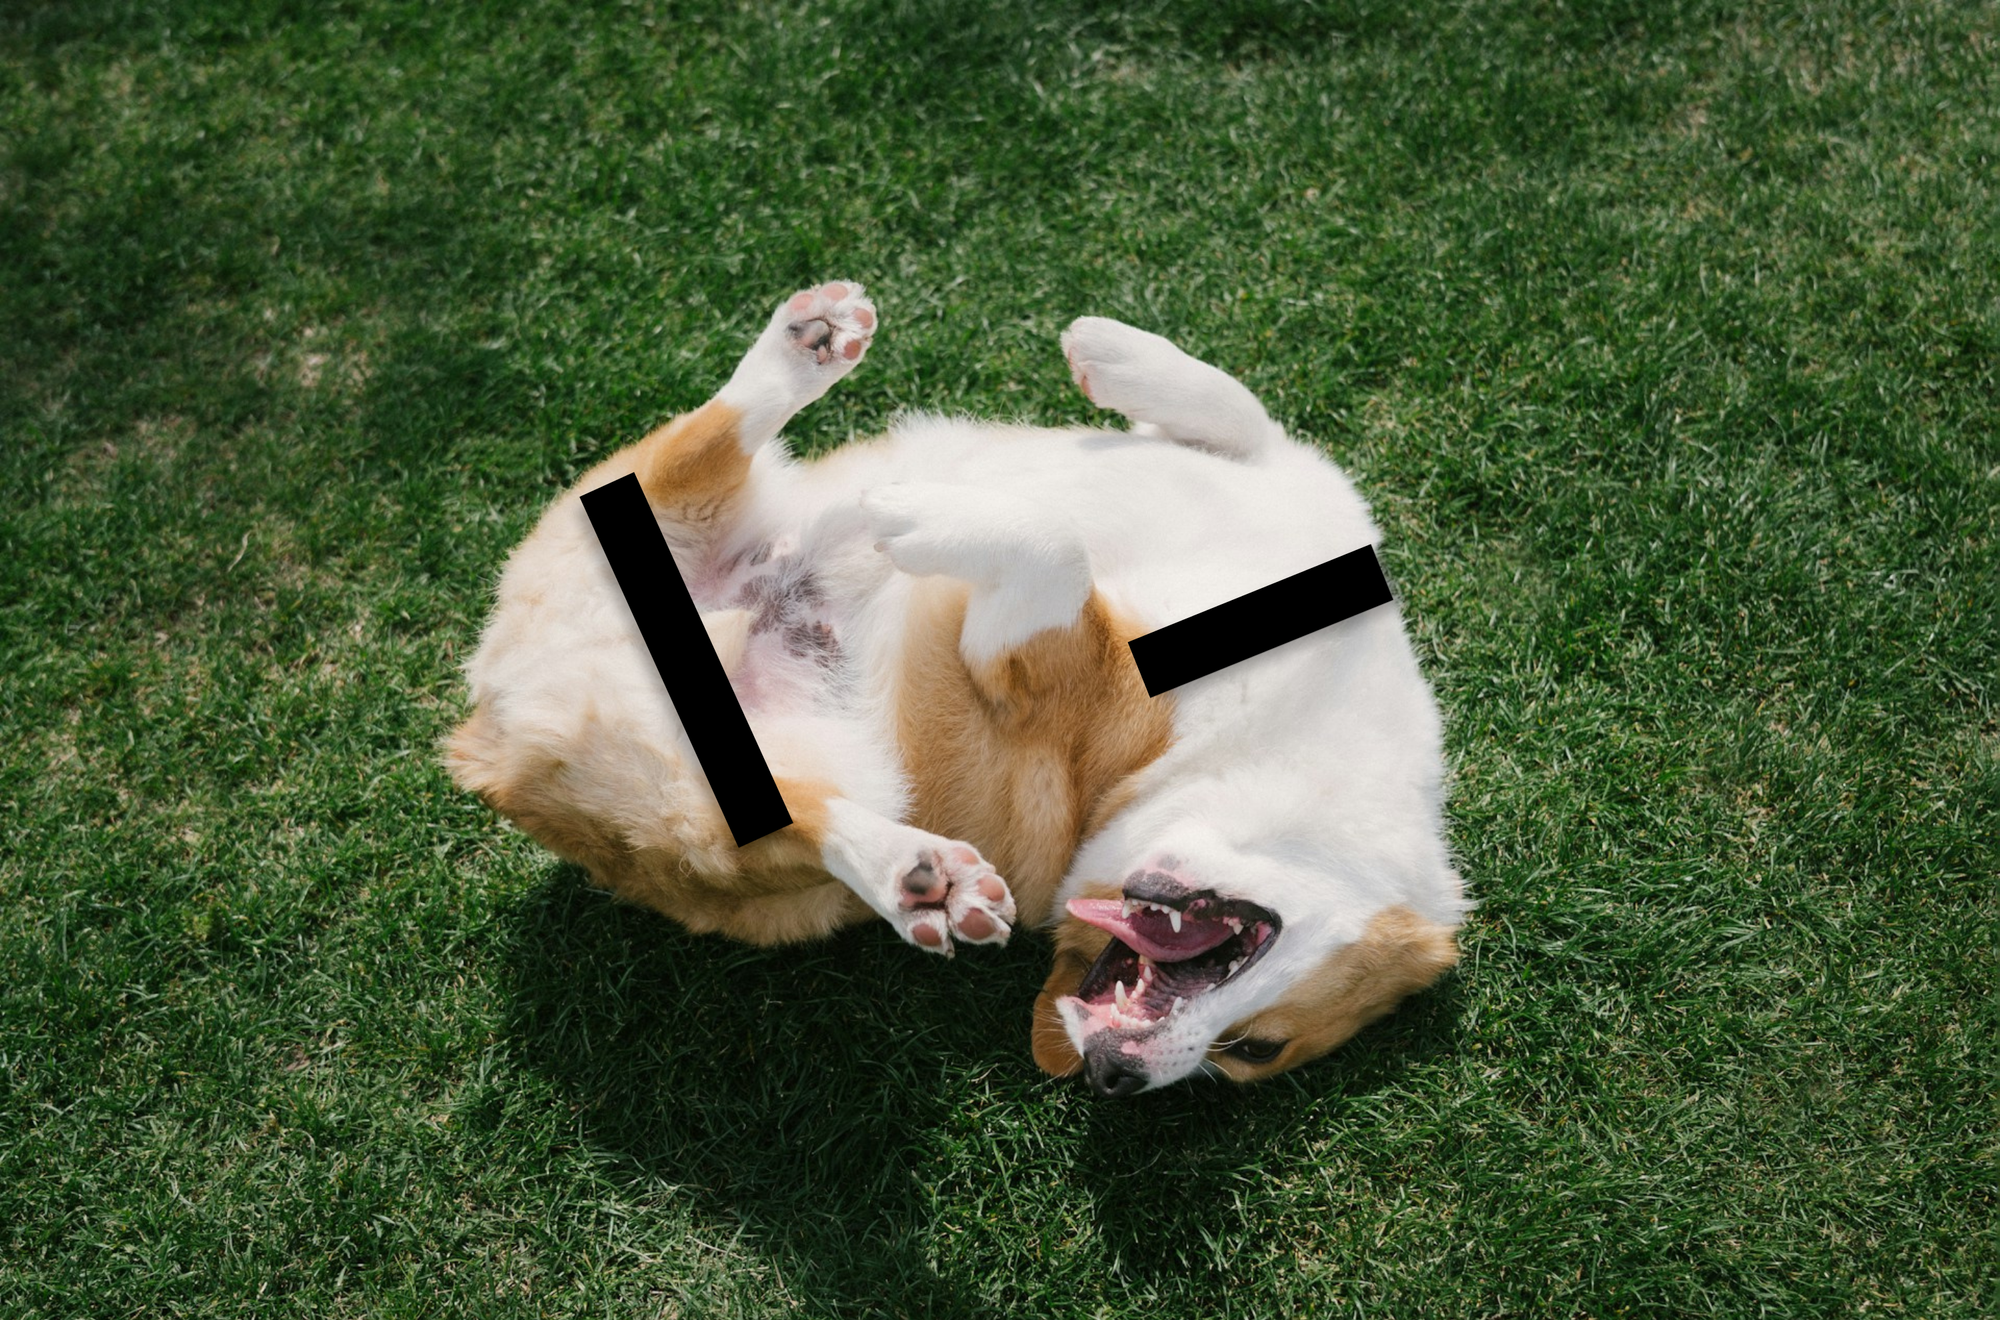
Image: 404 Media Apple’s iMessage Scanning Flagged a Video of My Friend's Dog as Nudity
In a video my friend’s dog is laying on her back, her little paws in the air, while my friend rubs the dog’s chest. You can see most of the dog — who I’m not naming for very important privacy reasons — from her head to her belly. On closer inspection, you’ll notice the picture includes some dog nipples. Apple’s iMessage thought this video was so inappropriate that it flagged the video as potentially containing nudity and blurred it. When someone else received the video over iMessage, the app displayed the message “This may be sensitive.” They had to purposefully tap to reveal the video of a…
Also in SANS Internet Storm Center Zero Day Initiative Zero Day Initiative +2
-
MCP gets an enterprise makeover
The Agentic AI Foundation, part of the Linux Foundation, has released an update to the Model Context Protocol (MCP) that aims to help enterprises adopt AI-based automation. Open-sourced by Anthropic in November 2024, MCP provides a way for AI applications (agents) based on models like GPT-5.6 Sol or Claude Opus 5 to connect to existing data sources, tools, or other applications. It defines how content is exchanged in a client-server architecture. "The new release is MCP’s most important since remote MCP first launched over a year ago," wrote David Soria Parra, a member of technical staff at…
Also in Schneier on Security The Hacker News Infosecurity Magazine
-
Stop rewriting detection rules by hand: automatic Sentinel-to-Elastic migration is here
Elastic automatically translates your Microsoft Sentinel detection rules into Elastic Security. Export your Scheduled and Near Real Time (NRT) analytics rules from Sentinel, upload them, and Elastic picks up the mapping and translation from there using an LLM you choose. Watchlists and severity mappings carry over. This is the first automatic migration path off a modern SIEM, available now in Tech Preview in 9.5, and it works across multiple cloud providers and regions so you can deploy closer to where your data lives. Which Microsoft Sentinel rule types can be migrated automatically?…
Also in The Register Security Dark Reading
-
73% of Organizations Say They Are Not Fully Ready for a Major Cyberattack
Most organizations have incident response plans, security tools, and technical teams in place. Yet new research suggests that many still lack the coordination, visibility, and executive alignment needed to withstand a serious cyberattack. According to The State of Incident Response Readiness 2026, based on a survey of 600 senior IT security decision makers conducted by Vanson Bourne in January
Also in CrowdStrike Blog

-
Public PoC Released for Exploited Check Point SmartConsole Authentication Bypass
Cybersecurity researchers have shared additional technical details about a recently patched critical security flaw impacting Check Point Security Management Server and Multi-Domain Security Management Server (MDS) that has come under active exploitation in the wild. The vulnerability, tracked as CVE-2026-16232 (CVSS score: 9.3), is an authentication bypass in the SmartConsole login process that
Also in Rapid7 Blog

Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| On CISA KEV 1added in the brief's window | |||||||||
| CVE-2026-20316 | Secure Firewall Management CenterCisco | Medium | 5.3 | 0.8% | KEV | — | — | KEVEPSS 0.8%CVSS 5.3 | |
What it isA vulnerability in the web interface of Cisco Secure Firewall Management Center (FMC) Software could allow an unauthenticated, remote attacker to log in to an affected device using a low-privileged account to access sensitive data within th… Attack
Exploitation
|
|||||||||
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-16498 | ToolingHashiCorp | Critical | 10.0 | 0.3% | — | — | — | EPSS 0.3%CVSS 10.0 | |
What it isThe terraform-mcp-server before version 1.1.0 is vulnerable to a cross-tenant credential reuse issue in the streamable-HTTP stateless transport mode that may allow one user's Terraform token to be used to execute tool calls on behalf of sub… Attack
Exploitation
|
|||||||||
| CVE-2026-33267 | Apache Traffic ServerApache | Critical | 10.0 | 0.2% | — | — | — | EPSS 0.2%CVSS 10.0 | |
What it isImproper Input Validation vulnerability in Apache Traffic Server. This issue affects Apache Traffic Server: from 9.2.0 through 9.2.14, from 10.1.0 through 10.1.3. Users are recommended to upgrade to version 9.2.15 or 10.1.4, which fixes t… Attack
Exploitation
|
|||||||||
| CVE-2026-57834 | Apache Traffic ServerApache | Critical | 10.0 | 0.3% | — | — | — | EPSS 0.3%CVSS 10.0 | |
What it isApache Traffic Server allows request smuggling if chunked messages are malformed. This issue affects Apache Traffic Server: from 8.0.0 through 8.1.9, from 9.0.0 through 9.2.14, from 10.0.0 through 10.1.3. Users are recommended to upgrade … Attack
Exploitation
|
|||||||||
| CVE-2026-58150 | Apache Traffic ServerApache | Critical | 10.0 | 0.2% | — | — | — | EPSS 0.2%CVSS 10.0 | |
What it isApache Traffic Server does not reject Transfer-Encoding in HTTP/2 requests, allowing downgrade request smuggling. This issue affects Apache Traffic Server: from 8.0.0 through 8.1.9, from 9.0.0 through 9.2.14, from 10.0.0 through 10.1.3. U… Attack
Exploitation
|
|||||||||
| CVE-2026-58162 | Apache Traffic ServerApache | Critical | 10.0 | 0.2% | — | — | — | EPSS 0.2%CVSS 10.0 | |
What it isThe Apache Traffic Server certifier plugin generates certificates based on attacker-controlled client SNI. This issue affects Apache Traffic Server: from 8.0.0 through 8.1.9, from 9.0.0 through 9.2.14, from 10.0.0 through 10.1.3. Users ar… Attack
Exploitation
|
|||||||||
| CVE-2026-63227 | Koollab LMSAn unrestricted SCORM file upload vulnerability in Koollab LMS allowed an authenticated module designer to upload a SCORM package containing a PHP webshell to a publicly accessible directory and execute arbitrary code on the server. | Critical | 9.9 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.9 | |
What it isAn unrestricted SCORM file upload vulnerability in Koollab LMS allowed an authenticated module designer to upload a SCORM package containing a PHP webshell to a publicly accessible directory and execute arbitrary code on the server. Attack
Exploitation
|
|||||||||
| CVE-2026-63232 | Koollab LMSThree Learning | Critical | 9.9 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.9 | |
What it isA SQL injection and unsafe deserialisation vulnerability in Koollab LMS allowed an authenticated attacker to inject through the assessment reinforcement endpoint, control data passed to unserialize(), write a webshell to a publicly accessib… Attack
Exploitation
|
|||||||||
| CVE-2026-63233 | Koollab LMSThree Learning | Critical | 9.9 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.9 | |
What it isA SQL injection and unsafe deserialisation vulnerability in Koollab LMS allowed an authenticated attacker to inject through the assessment overall answer endpoint, control data passed to unserialize(), write a webshell to a publicly accessi… Attack
Exploitation
|
|||||||||
| CVE-2026-63234 | Koollab LMSThree Learning | Critical | 9.9 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.9 | |
What it isA SQL injection and unsafe deserialisation vulnerability in Koollab LMS allowed an authenticated attacker to inject through the manual mark assessment endpoint, control data passed to unserialize(), write a webshell to a publicly accessible… Attack
Exploitation
|
|||||||||
| CVE-2026-51252 | Unknown | Critical | 9.8 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.8 | |
What it isschreibfaul1 ESP32-audioI2S 3.4.5 has a buffer overflow vulnerability in the MP3Decoder::UnpackSFMPEG1 function due to missing input validation on attacker-controlled MP3 metadata. Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.