Friday, July 31, 2026 · generated · about 6 min read
Morning Brief
Patch today vendors with the most new CVEs today
- HashiCorp 1 critical 56
- WordPress 1 critical 37
- Unknown 3 critical 25
- IBM 5 critical 23
- Red Hat 19
- Apache 16
- Microsoft 1 critical 6
- SGLang 6
- cloudreve 6
- MZ Automation GmbH 5
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-

Image: The Hacker News Three Recent Chrome Releases Fix 1,442 Flaws, More Than Prior 23 Updates Combined
Google on Thursday announced that it fixed a whopping 1,072 security bugs in Chrome versions 149 and 150, surpassing the total number of flaws the company fixed across the prior 23 milestones combined. Both versions were released last month. In its latest patch for Chrome 151, released Wednesday, the tech giant resolved 370 flaws, out of which 349 were reported by Google itself. Seven of the
Also in Cyber Security News SecurityWeek Bleeping Computer +3
-
Azure Cosmos DB Flaw Exposed Platform-Wide Key That Could Access Any Database
A now-patched vulnerability in Azure Cosmos DB could have let an attacker escape the service's Gremlin query sandbox and obtain full read and write access to databases across customer tenants, according to Wiz. Wiz, which codenamed the chain CosmosEscape, said the exploit chain began with a crafted query against a Gremlin database controlled by the attacker. From there, code execution on a
Also in SecurityWeek Microsoft Security Microsoft Security +2

-
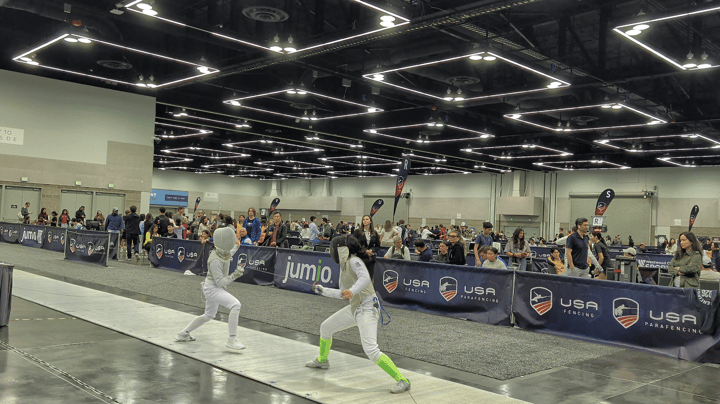
USA Fencing Lunges Into the Hidden Identity Challenge in Amateur Sports
The organization behind Team USA's Olympic/Paralympic fencing teams has automated identity verification to handle growing membership, cutting manual review time while ensuring athletes compete in the correct categories.
Also in Dark Reading The Hacker News Recorded Future Intelligence +3
-
Microsoft Copilot for Word Can Copy Hidden Prompts Into New Documents
Hidden instructions in a Word document can make Microsoft 365 Copilot rewrite figures in a report, then copy the same instructions into the finished file. Håkon Måløy disclosed the technique on July 28, 144 days after reporting it to Microsoft. In his proof of concept, the internally generated file triggered the same behavior when it was used in a second Copilot drafting session. Måløy's
Also in Malwarebytes Labs Bleeping Computer Malwarebytes Labs +3

-
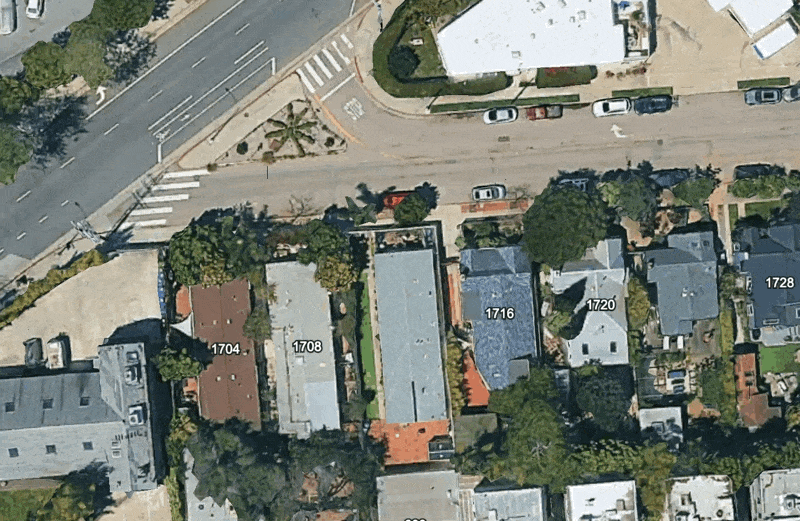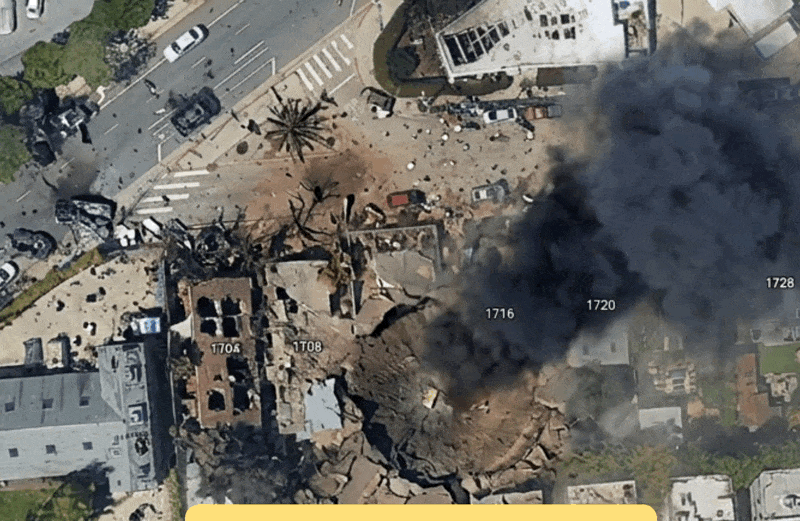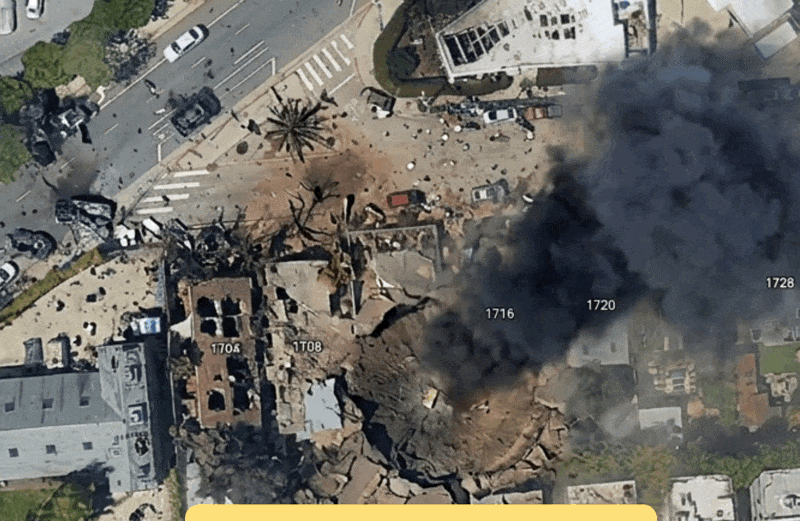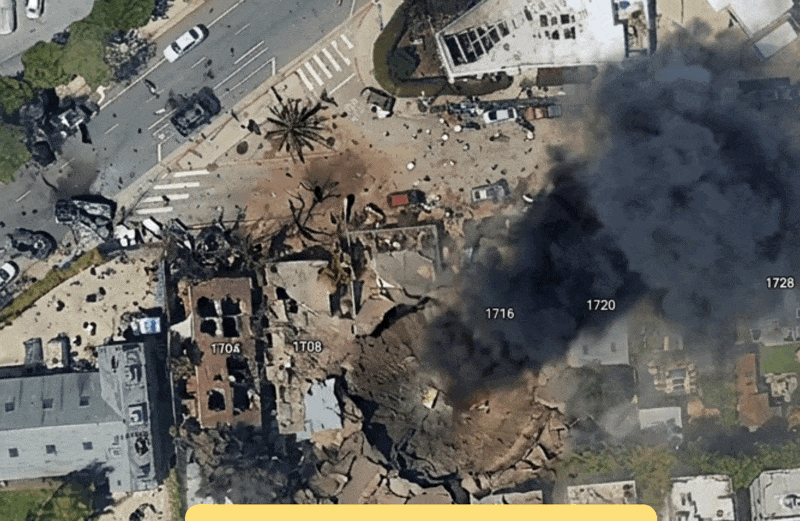
Google Earth’s New AI Lets Anyone Fabricate Completely Bullshit Satellite Images
On Thursday, Google introduced a new AI feature into Google Earth which lets anyone fabricate all sorts of misleading or straight up inaccurate satellite imagery, from making it look like a specific place has suffered a drone strike to manifesting a nuclear plant in Iran. Usually, Google Earth is an exceptionally useful tool for open source intelligence (OSINT) analysts to digitally monitor areas of interest and see how they change over time, say, during a conflict or disaster. Now, Google Earth can easily be used as a tool for disinformation. In 404 Media’s tests, we were able to add…
Also in CCCS Alerts & Advisories Wiz Research
-
Critical JetBrains Flaw Allows Attackers to Execute Malicious Code Remotely – Update Now
JetBrains has announced a critical vulnerability in TeamCity On-Premises, identified as CVE-2026-63077 . This vulnerability allows attackers to bypass authentication and execute arbitrary commands remotely. It affects all versions of TeamCity On-Premises. An attacker only requires HTTP or HTTPS access to a vulnerable TeamCity server to exploit this issue, with no need for a valid account, password, or prior access. According to JetBrains, the flaw resides in the TeamCity agent polling protocol. A remote attacker can use this protocol to bypass authentication checks and execute operating…
Also in SecurityWeek Rapid7 Blog

-
North Korean EtherHiding Campaign Targets Crypto Wallets and Developer Credentials
A North Korean-linked cyber campaign is using fake macOS update screens to trick victims into installing malware. The operation targets cryptocurrency wallets, browser data, and developer credentials, turning a routine web search into a possible entry point for a serious compromise. The attack begins with a ClickFix-style lure that makes a browser page look like a frozen or rebooting Mac. Victims are told to open Terminal and paste a command that the malicious page has already copied to their clipboard, allowing the infection chain to start. AllSecure analysts identified the activity while…
Also in Palo Alto Unit 42 The Hacker News

-
BlackTech APT Deploys BlueShell Linux Backdoor Against Japanese Organizations
BlackTech has been linked to a newly examined Linux backdoor deployment against organizations in Japan, showing how a familiar remote-access tool can be reshaped for cyberespionage. The malware gives intruders a way to run commands, move files, and route traffic after they have already entered a network, raising the risk to internal systems and sensitive data. The attack begins after the attackers gain access and move laterally through the victim environment using SSH. From there, they deploy a loader that launches the backdoor, a method that reflects the group’s established interest in…
Also in Cyber Security News Infosecurity Magazine Schneier on Security

-
ShutterGap Exposes Millions of AWS Resources Between Cloud Security Scans
Cloud security teams often utilize Cloud Security Posture Management (CSPM) and Cloud-Native Application Protection Platform (CNAPP) tools to identify risky configurations. However, new research from Aryon Security reveals that this approach may overlook a significant class of threats: temporary AWS resources that are publicly exposed but removed before the next scan occurs. Aryon refers to this visibility gap as “ShutterGap.” It happens when a cloud resource is made public for a brief period, sometimes lasting only a few minutes. Attackers can continuously monitor public AWS resources…
Also in Infosecurity Magazine SecurityWeek

-
North Korean hackers behind major open-source supply chain attacks, Amazon says
A North Korea-linked hacker group was behind several high-profile compromises of open-source software libraries used by developers worldwide, researchers have found.
Also in Bleeping Computer The Hacker News CyberScoop

Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-66803 | Azure Cosmos DBMicrosoft | Critical | 10.0 | 0.5% | — | — | — | EPSS 0.5%CVSS 10.0 | |
What it isImproper access control in Azure Cosmos DB allows an unauthorized attacker to execute code over a network. Attack
Exploitation
|
|||||||||
| CVE-2026-18452 | DMS+ (Non-Mobile)Rich Source | Critical | 10.0 | 0.4% | — | — | — | EPSS 0.4%CVSS 10.0 | |
What it isDMS+ (Non-Mobile) developed by Rich Source has a Use of Hard-coded Credentials vulnerability. Unauthenticated remote attackers can exploit a fixed API key to gain control over all installed DMS+ devices. Attack
Exploitation
|
|||||||||
| CVE-2026-13435 | Langflow OSSIBM | Critical | 9.9 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.9 | |
What it isIBM Langflow OSS 1.0.0 through 1.10.1 contains an improper input validation vulnerability in the PythonREPL sandbox implementation. Attack
Exploitation
|
|||||||||
| CVE-2026-12946 | Langflow OSSIBM | Critical | 9.9 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.9 | |
What it isIBM Langflow OSS 1.0.0 through 1.10.0 could allow a remote attacker to inject arbitrary code on the system, due to the improper control of user input code. Attack
Exploitation
|
|||||||||
| CVE-2026-28323 | Web Help DeskSolarWinds | Critical | 9.8 | 0.6% | — | — | — | EPSS 0.6%CVSS 9.8 | |
What it isSolarWinds Web Help Desk is found to be affected by a SAML authentication bypass vulnerability. This requires the SAML 2.0 authentication method to be enabled. Attack
Exploitation
|
|||||||||
| CVE-2026-4978 | Traffic Analysis SystemUMAI Vision | Critical | 9.8 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.8 | |
What it isImproper neutralization of special elements used in an SQL command ('SQL injection') vulnerability in UMAI Vision Traffic Analysis System allows SQL Injection. This issue affects Traffic Analysis System: from 30 before 34. Attack
Exploitation
|
|||||||||
| CVE-2026-12940 | Langflow OSSIBM | Critical | 9.8 | 0.5% | — | — | — | EPSS 0.5%CVSS 9.8 | |
What it isIBM Langflow OSS 1.0.0 through 1.10.1 are vulnerable to unauthenticated remote code execution via environment variable injection in the MCP (Model Context Protocol) stdio launcher. The vulnerability exists in src/lfx/src/lfx/base/mcp/util.… Attack
Exploitation
|
|||||||||
| CVE-2026-12118 | webMethods Integration (on prem)IBM | Critical | 9.8 | 0.5% | — | — | — | EPSS 0.5%CVSS 9.8 | |
What it isIBM webMethods Integration (on prem) 10.15, 10.11 could allow an unauthenticated remote attacker to execute arbitrary code on the system due to the deserialization of untrusted data. Attack
Exploitation
|
|||||||||
| CVE-2026-12943 | HMC V10.3.1050.0IBM | Critical | 9.8 | 0.9% | — | — | — | EPSS 0.9%CVSS 9.8 | |
What it isIBM HMC V10.3.1050.0 through 10.3.1064.0 and IBM HMC V11.1.1110.0 through 11.1.1112.0 Management systems in IBM Power environments (HMC and Novalink) could allow an unauthenticated user to execute arbitrary commands with elevated privileges… Attack
Exploitation
|
|||||||||
| CVE-2026-67208 | Jugglesomta | Critical | 9.8 | 1% | — | — | — | EPSS 1%CVSS 9.8 | |
What it isJuggle through 1.6.0 contains a remote code execution vulnerability that allows unauthenticated remote attackers to execute arbitrary OS commands by connecting to the exposed H2 database web console using default shipped credentials. Attack… Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Worth reading quieter, still worth your time
-
Critical VMware vCenter Vulnerabilities Allow Authentication Bypass and Remote Code Execution (CVE-2026-59309, CVE-2026-59310)
Overview On July 29, 2026, Broadcom published security advisory VMSA-2026-0006 addressing multiple vulnerabilities in several VMWare products. Included in the advisory are two critical remotely exploitable vulnerabilities affecting VMware vCenter Server: CVE-2026-59309 and CVE-2026-59310. Both vulnerabilities carry CVSSv3.1 base scores of 9.8 and can be exploited by unauthenticated attackers with network access to a vulnerable vCenter Server. CVE CVSSv3.1 Description Summary CVE-2026-59309 9.8 (Critical) An authentication bypass vulnerability in the VMware Directory Service of vCenter that…
Also in Bleeping Computer The Hacker News

-
Max-severity Exchange server flaw under active exploitation by Kremlin hackers
Russian state hackers are using a maximum-severity vulnerability in Microsoft Outlook’s Exchange Server to backdoor unpatched machines and steal credentials and other confidential information from them, security researchers said Thursday. The attacks are coming from TA488, a tracking name for a group working on behalf of the Kremlin, Proofpoint researchers said Thursday . Proofpoint and the National Security Agency jointly warned last week that the group, also tracked as Laundry Bear and Void Blizzard, had been carrying out similar attacks by exploiting a zero-day vulnerability in an email…
Also in Bleeping Computer
-
ZDI-26-495: (Pwn2Own) VMware ESXi VMXNET3 espQueueMask Out-Of-Bounds Write Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of VMware ESXi. An attacker must first obtain the ability to execute high-privileged code on the target guest system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.2. The following CVEs are assigned: CVE-2026-47876.
Also in CCCS Alerts & Advisories
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.