Saturday, August 1, 2026 · generated · about 6 min read
Morning Brief
Patch today vendors with the most new CVEs today
- HashiCorp 1 critical 48
- WordPress 3 critical 43
- Unknown 1 critical 20
- Red Hat 15
- pgadmin.org 3 critical 6
- PHP Jabbers 5
- HCL Software 5
- thumbor 5
- ANDRITZ 4
- decidim 4
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-

Image: The Hacker News Hijacked Hotel Wi-Fi Pushes Fake Updates to Deliver Surveillance Malware
A fake browser update served over hijacked hotel Wi-Fi has been used to deliver CornFlake, a remote access trojan (RAT) that can capture webcam images, microphone audio, and keystrokes, Microsoft said in its latest report. Researchers track the operation as CaptiveCrunch and attribute it to Storm-2945. It assesses Storm-2945 to be an operational sub-cluster of Midnight Blizzard, also known as
Also in Malwarebytes Labs Bleeping Computer Malwarebytes Labs +3
-
Three Recent Chrome Releases Fix 1,442 Flaws, More Than Prior 23 Updates Combined
Google on Thursday announced that it fixed a whopping 1,072 security bugs in Chrome versions 149 and 150, surpassing the total number of flaws the company fixed across the prior 23 milestones combined. Both versions were released last month. In its latest patch for Chrome 151, released Wednesday, the tech giant resolved 370 flaws, out of which 349 were reported by Google itself. Seven of the
Also in Cyber Security News SecurityWeek Bleeping Computer +3

-
Arch Linux Disables AUR Package Takeovers as Attackers Push Malicious Commits
Arch Linux has temporarily disabled package adoption on its Arch User Repository (AUR) after security teams detected a wave of malicious takeovers and follow-up commits designed to compromise unsuspecting users. The move, announced by Robin Candau (known online as Antiz) on behalf of the Arch Linux DevOps team, comes as attackers increasingly exploit an abandoned or unmaintained package as an entry point for supply-chain attacks. Last month, a massive supply chain attack targeting the Arch User Repository (AUR) compromised more than 400 community-maintained packages , with attackers injecting…
Also in Bleeping Computer Cyber Security News Infosecurity Magazine +1

-
Adobe Campaign Classic CVSS 10.0 Flaw Could Run Code Without User Interaction
Adobe has released security updates to address a maximum-severity security flaw in Campaign Classic (ACC), its enterprise-focused marketing automation platform, that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-48449, carries a severity score of 10.0 on the CVSS scoring system. It has been described as a case of incorrect authorization that could result in
Also in SecurityWeek CCCS Alerts & Advisories CCCS Alerts & Advisories

-
Azure Cosmos DB Flaw Exposed Platform-Wide Key That Could Access Any Database
A now-patched vulnerability in Azure Cosmos DB could have let an attacker escape the service's Gremlin query sandbox and obtain full read and write access to databases across customer tenants, according to Wiz. Wiz, which codenamed the chain CosmosEscape, said the exploit chain began with a crafted query against a Gremlin database controlled by the attacker. From there, code execution on a
Also in SecurityWeek Microsoft Security Microsoft Security +2

-
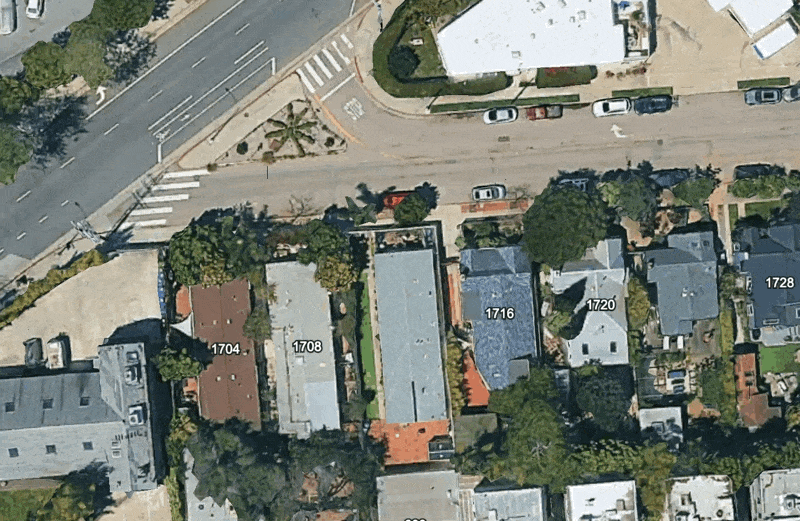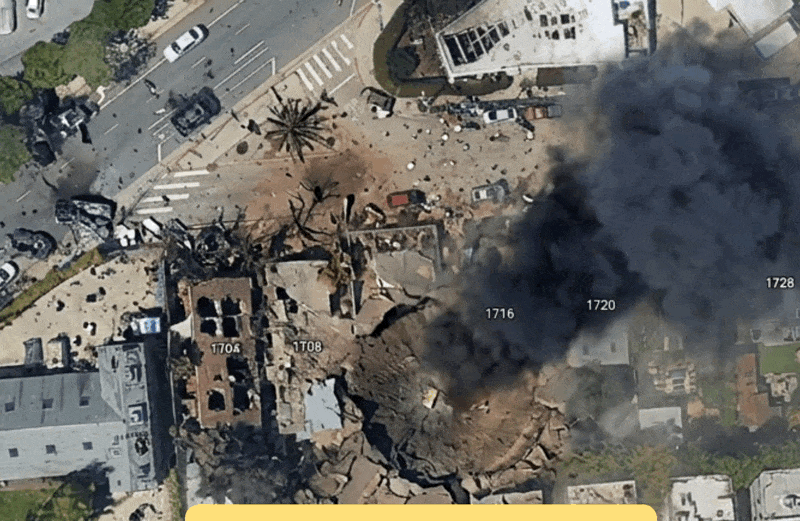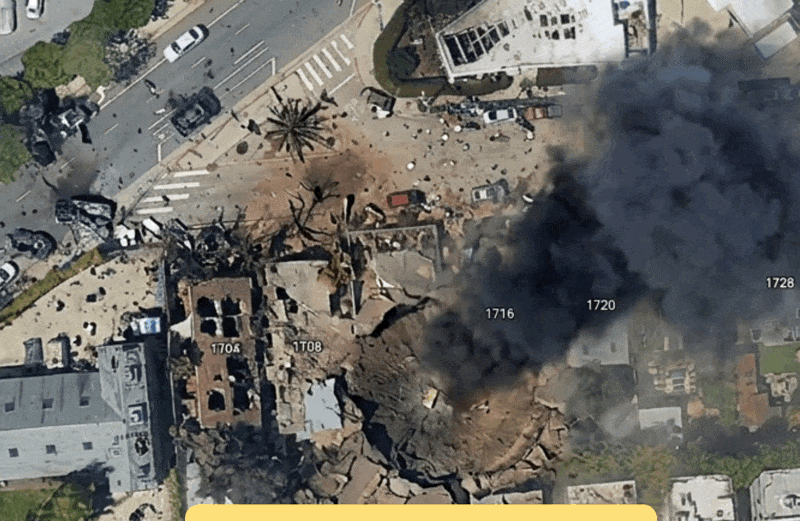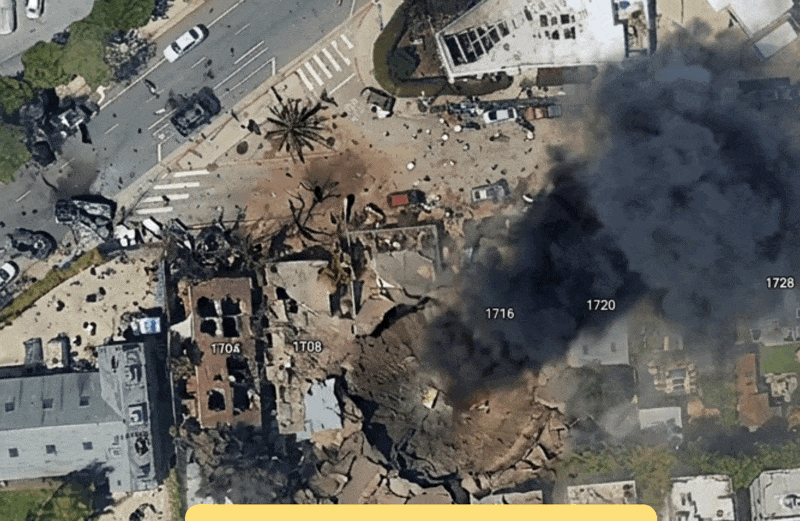
Google Earth’s New AI Lets Anyone Fabricate Completely Bullshit Satellite Images
On Thursday, Google introduced a new AI feature into Google Earth which lets anyone fabricate all sorts of misleading or straight up inaccurate satellite imagery, from making it look like a specific place has suffered a drone strike to manifesting a nuclear plant in Iran. Usually, Google Earth is an exceptionally useful tool for open source intelligence (OSINT) analysts to digitally monitor areas of interest and see how they change over time, say, during a conflict or disaster. Now, Google Earth can easily be used as a tool for disinformation. 💡 Do you work at Google? I would love to hear…
Also in CCCS Alerts & Advisories Wiz Research
-
Critical JetBrains Flaw Allows Attackers to Execute Malicious Code Remotely – Update Now
JetBrains has announced a critical vulnerability in TeamCity On-Premises, identified as CVE-2026-63077 . This vulnerability allows attackers to bypass authentication and execute arbitrary commands remotely. It affects all versions of TeamCity On-Premises. An attacker only requires HTTP or HTTPS access to a vulnerable TeamCity server to exploit this issue, with no need for a valid account, password, or prior access. According to JetBrains, the flaw resides in the TeamCity agent polling protocol. A remote attacker can use this protocol to bypass authentication checks and execute operating…
Also in SecurityWeek Rapid7 Blog

-
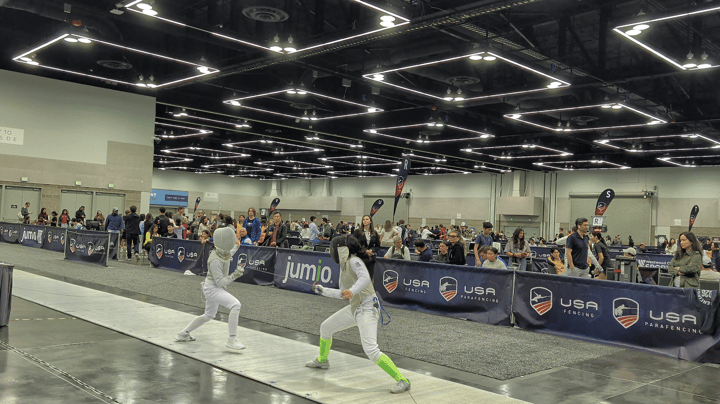
USA Fencing Lunges Into the Hidden Identity Challenge in Amateur Sports
The organization behind Team USA's Olympic/Paralympic fencing teams has automated identity verification to handle growing membership, cutting manual review time while ensuring athletes compete in the correct categories.
Also in Dark Reading The Hacker News Recorded Future Intelligence +1
-
North Korean EtherHiding Campaign Targets Crypto Wallets and Developer Credentials
A North Korean-linked cyber campaign is using fake macOS update screens to trick victims into installing malware. The operation targets cryptocurrency wallets, browser data, and developer credentials, turning a routine web search into a possible entry point for a serious compromise. The attack begins with a ClickFix-style lure that makes a browser page look like a frozen or rebooting Mac. Victims are told to open Terminal and paste a command that the malicious page has already copied to their clipboard, allowing the infection chain to start. AllSecure analysts identified the activity while…
Also in Palo Alto Unit 42 The Hacker News

-
Critical VMware vCenter Vulnerabilities Allow Authentication Bypass and Remote Code Execution (CVE-2026-59309, CVE-2026-59310)
Overview On July 29, 2026, Broadcom published security advisory VMSA-2026-0006 addressing multiple vulnerabilities in several VMWare products. Included in the advisory are two critical remotely exploitable vulnerabilities affecting VMware vCenter Server: CVE-2026-59309 and CVE-2026-59310. Both vulnerabilities carry CVSSv3.1 base scores of 9.8 and can be exploited by unauthenticated attackers with network access to a vulnerable vCenter Server. CVE CVSSv3.1 Description Summary CVE-2026-59309 9.8 (Critical) An authentication bypass vulnerability in the VMware Directory Service of vCenter that…
Also in Bleeping Computer The Hacker News

Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-18452 | DMS+ (Non-Mobile)Rich Source | Critical | 10.0 | 0.4% | — | — | — | EPSS 0.4%CVSS 10.0 | |
What it isDMS+ (Non-Mobile) developed by Rich Source has a Use of Hard-coded Credentials vulnerability. Unauthenticated remote attackers can exploit a fixed API key to gain control over all installed DMS+ devices. Attack
Exploitation
|
|||||||||
| CVE-2026-17566 | pgAdmin 4pgadmin.org | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it ispgAdmin 4's Import/Export Data tool builds a psql \copy (...) command line by interpolating a user-supplied SQL query into a Jinja template and passing the rendered line to psql via --command. To stop an attacker from breaking out of the (.… Attack
Exploitation
|
|||||||||
| CVE-2026-52855 | wingspterodactyl | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isWings is the server control plane for Pterodactyl, a free, open-source game server management panel. Prior to 1.12.3, {{config.}} placeholders in egg configuration-file templates allow a low-privileged user to read {{config.token}}, {{confi… Attack
Exploitation
|
|||||||||
| CVE-2026-14483 | Realtyna Organic IDX plugin + WPL Real EstateWordPress | Critical | 9.8 | 0.6% | — | — | — | EPSS 0.6%CVSS 9.8 | |
What it isThe Realtyna Organic IDX plugin + WPL Real Estate plugin for WordPress is vulnerable to Arbitrary File Upload in all versions up to, and including, 5.2.0 via the upload function. This is due to missing file type validation in the upload fun… Attack
Exploitation
|
|||||||||
| CVE-2026-14919 | ShopMonitor.ioWordPress | Critical | 9.8 | 0.1% | — | — | — | EPSS 0.1%CVSS 9.8 | |
What it isThe ShopMonitor.io WordPress plugin before 1.2.0 does not properly restrict its email-rerouting test mode, gating it behind a trusted-source check that is satisfiable with client-supplied request headers, allowing unauthenticated attackers… Attack
Exploitation
|
|||||||||
| CVE-2026-17561 | Logsign SIEMHashiCorp | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isImproper Control of Generation of Code ('Code Injection') vulnerability in Innotim Software, Telecommunications and Consulting Trade Ltd. Co. Logsign SIEM allows Code Injection. This issue affects Logsign SIEM: before 6.4.108. Attack
Exploitation
|
|||||||||
| CVE-2026-67822 | Unknown | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isTenda W6-S 1.0.0.4(510) contains a stack-based buffer overflow vulnerability in the /goform/wifiSSIDset endpoint. The function formwrlSSIDset uses sprintf to copy user-controlled 'GO' and 'index' parameters into a 64-byte stack buffer witho… Attack
Exploitation
|
|||||||||
| CVE-2026-68770 | sentence-transformersHugging Face | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it issentence-transformers contains a security control bypass vulnerability that allows attackers to achieve arbitrary code execution by exploiting a logic flaw in the import_module_class helper within sentence_transformers/util/misc.py, where t… Attack
Exploitation
|
|||||||||
| CVE-2026-68771 | ComfyUIComfy-Org | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isComfyUI v0.23.0 contains an unsafe deserialization vulnerability in the LoadTrainingDataset node that allows unauthenticated remote attackers to execute arbitrary Python code by uploading a crafted pickle file and triggering its deserializa… Attack
Exploitation
|
|||||||||
| CVE-2026-17349 | pgAdmin 4pgadmin.org | Critical | 9.6 | — | — | — | — | CVSS 9.6 | |
What it is/misc/workspace/adhoc_connect_server, part of the Workspaces feature introduced in pgAdmin 4 9.0, when passed the id of an existing server, clones that server via Server.clone(), which copies every column from the source row, including user… Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Worth reading quieter, still worth your time
-
Max-severity Exchange server flaw under active exploitation by Kremlin hackers
Russian state hackers are using a maximum-severity vulnerability in Microsoft Outlook’s Exchange Server to backdoor unpatched machines and steal credentials and other confidential information from them, security researchers said Thursday. The attacks are coming from TA488, a tracking name for a group working on behalf of the Kremlin, Proofpoint researchers said Thursday . Proofpoint and the National Security Agency jointly warned last week that the group, also tracked as Laundry Bear and Void Blizzard, had been carrying out similar attacks by exploiting a zero-day vulnerability in an email…
Also in Proofpoint Threat Insight
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.