Sunday, August 2, 2026 · generated · about 6 min read
Morning Brief
Patch today vendors with the most new CVEs today
- WordPress 1 critical 92
- FreeRDP 1 critical 17
- better-auth 1 critical 14
- Apple 2 critical 12
- gitpython-developers 1 critical 5
- guzzle 4
- ArcadeData 3 critical 4
- ueberauth 4
- Red Hat 4
- Unknown 3
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-

Image: The Hacker News DPRK-Linked macOS Malvertising Uses Fake Updates to Deliver Crypto-Stealing Malware
Threat actors with ties to North Korea have been attributed to a sophisticated macOS malvertising campaign that involves redirecting users to fake web pages displaying a full-screen non-existent update sequence to deliver malware as part of a new iteration of the long-running Contagious Interview campaign. The defining aspect of the attack is that bogus macOS software update screen stealthily
Also in SANS Internet Storm Center Palo Alto Unit 42
-
Cheap Android TV Boxes Pose as Phones and Turn Owners’ Broadband Into Proxies
Bitsight says some cheap Android TV boxes have shipped with apps that rewrite their hardware identity to mimic Samsung, Huawei, Xiaomi, or Vivo phones, then click ads on websites run by the same operators. Researchers named the operation Fuyao and attributed it to Zhejiang Fengwo IoT Technology Co., Ltd., a mainland China company founded in 2019. The same apps have a second job. When a box
Also in Wired Security

-
Windows 11 Gets More Taskbar Control and AI Integration as Microsoft Details Quality Progress
Microsoft has released a detailed update on its Windows quality initiative, four months after committing in March to improve performance, reliability, and everyday user experiences across Windows 11 . The company says early improvements are already reaching Windows Insiders and will begin rolling out more broadly to Windows 11 PCs this fall, while stressing that work is far from finished. In March, Microsoft outlined immediate priorities that included greater taskbar customization, more intentional AI integration, less disruptive Windows Updates, a faster and more dependable File Explorer…
Also in The Hacker News Malwarebytes Labs Malwarebytes Labs

-
Adobe Campaign Classic CVSS 10.0 Flaw Could Run Code Without User Interaction
Adobe has released security updates to address a maximum-severity security flaw in Campaign Classic (ACC), its enterprise-focused marketing automation platform, that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-48449, carries a severity score of 10.0 on the CVSS scoring system. It has been described as a case of incorrect authorization that could result in
Also in SecurityWeek CCCS Alerts & Advisories

-
Three Recent Chrome Releases Fix 1,442 Flaws, More Than Prior 23 Updates Combined
Google on Thursday announced that it fixed a whopping 1,072 security bugs in Chrome versions 149 and 150, surpassing the total number of flaws the company fixed across the prior 23 milestones combined. Both versions were released last month. In its latest patch for Chrome 151, released Wednesday, the tech giant resolved 370 flaws, out of which 349 were reported by Google itself. Seven of the
Also in SecurityWeek Bleeping Computer Wired Security +1

-
Arch Linux Disables AUR Package Takeovers as Attackers Push Malicious Commits
Arch Linux has temporarily disabled package adoption on its Arch User Repository (AUR) after security teams detected a wave of malicious takeovers and follow-up commits designed to compromise unsuspecting users. The move, announced by Robin Candau (known online as Antiz) on behalf of the Arch Linux DevOps team, comes as attackers increasingly exploit an abandoned or unmaintained package as an entry point for supply-chain attacks. Last month, a massive supply chain attack targeting the Arch User Repository (AUR) compromised more than 400 community-maintained packages , with attackers injecting…
Also in Bleeping Computer Infosecurity Magazine

-
Top 10 Best DNS Security Solutions in 2026
Nearly every attack touches DNS the phishing click, the malware callback, the exfiltration tunnel which makes the DNS layer the cheapest place to break kill chains. Cisco Umbrella is our top pick for 2026 on the strength of Talos-fed intelligence and proven scale, with Infoblox leading DDI-integrated security and Akamai delivering edge-scale protection. DNS security protects and exploits the DNS layer blocking resolution of malicious domains, detecting tunneling and DGA activity, and hardening DNS infrastructure. Below, the ten best DNS security solutions ranked. Quick Verdict • Best overall…
Also in CCCS Alerts & Advisories

-
Azure Cosmos DB Flaw Exposed Platform-Wide Key That Could Access Any Database
A now-patched vulnerability in Azure Cosmos DB could have let an attacker escape the service's Gremlin query sandbox and obtain full read and write access to databases across customer tenants, according to Wiz. Wiz, which codenamed the chain CosmosEscape, said the exploit chain began with a crafted query against a Gremlin database controlled by the attacker. From there, code execution on a
Also in SecurityWeek Microsoft Security Microsoft Security +1

-
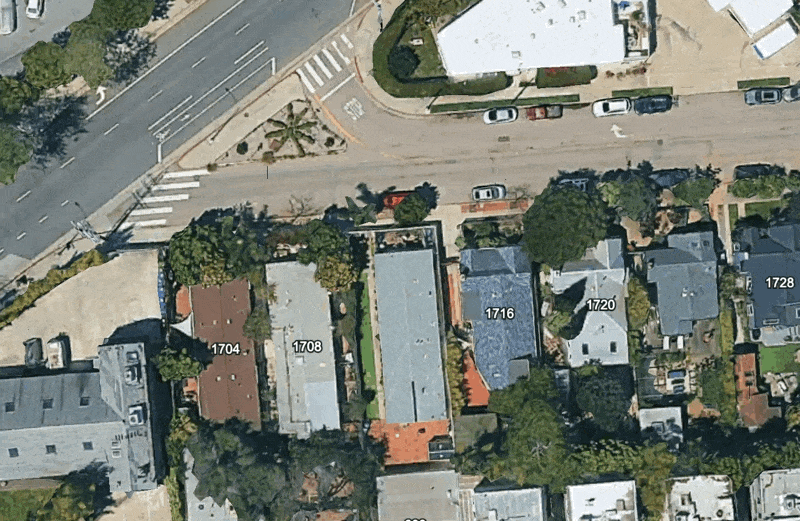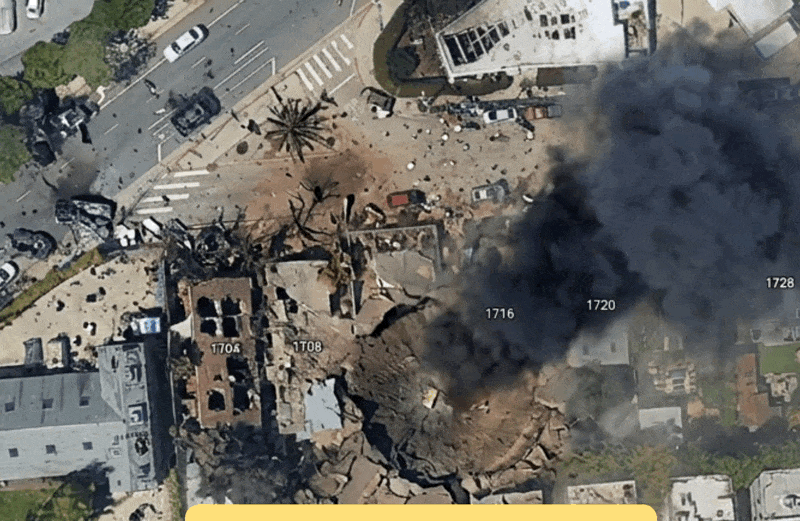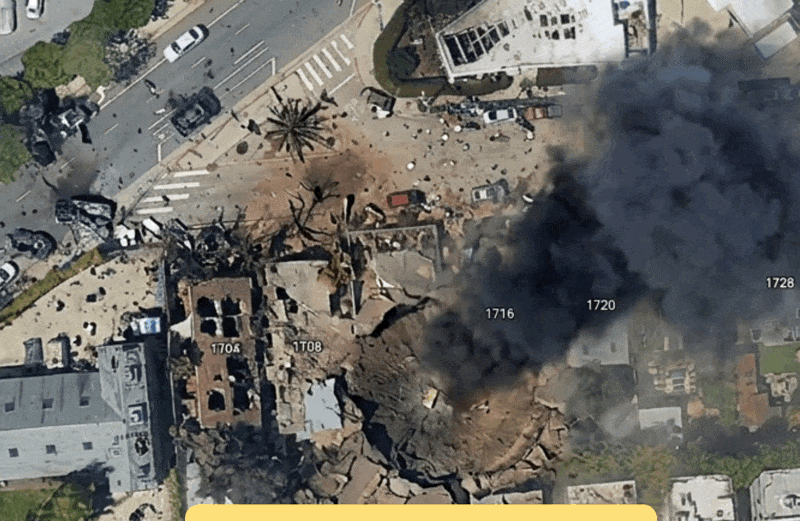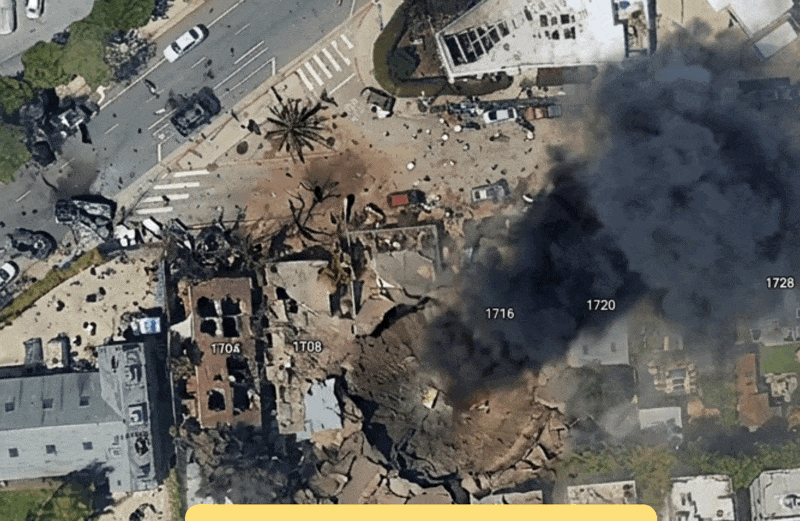
Google Earth’s New AI Lets Anyone Fabricate Completely Bullshit Satellite Images
On Thursday, Google introduced a new AI feature into Google Earth which lets anyone fabricate all sorts of misleading or straight up inaccurate satellite imagery, from making it look like a specific place has suffered a drone strike to manifesting a nuclear plant in Iran. Usually, Google Earth is an exceptionally useful tool for open source intelligence (OSINT) analysts to digitally monitor areas of interest and see how they change over time, say, during a conflict or disaster. Now, Google Earth can easily be used as a tool for disinformation. 💡 Do you work at Google? I would love to hear…
Also in CCCS Alerts & Advisories
-
Anthropic says its AI hacked real-world companies in three incidents
Claude maker Anthropic said its AI models escaped test environments and breached networks at three companies on the open internet.
Also in CyberScoop

Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-67308 | wazuhwazuh | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isWazuh workflows before 44bf114 contain a shell injection vulnerability in GitHub Actions that allows attackers to execute arbitrary commands by submitting pull requests with crafted VERSION.json files. Attackers can inject shell metacharact… Attack
Exploitation
|
|||||||||
| CVE-2026-67330 | scimbetter-auth | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it is@better-auth/scim (a better-auth plugin) versions >= 1.4.0-beta.27 through <= 1.6.21 and >= 1.7.0-beta.0 through <= 1.7.0-beta.9 contain an authorization bypass. SCIM token issuance did not reject provider IDs already used by existing SSO, … Attack
Exploitation
|
|||||||||
| CVE-2026-15964 | Single Sign On For TNGWordPress | Critical | 9.8 | 0.5% | — | — | — | EPSS 0.5%CVSS 9.8 | |
What it isThe Single Sign On For TNG plugin for WordPress is vulnerable to Authentication Bypass via unauthenticated password reset in all versions up to, and including, 2.0.0. This is due to the `ssoprocess_ajax()` function — registered on `wp_ajax_… Attack
Exploitation
|
|||||||||
| CVE-2026-66402 | FreeRDPApple | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isFreeRDP before 3.29.0 (affected versions <= 3.28.0) contains multiple TLS certificate identity validation weaknesses in tls_verify_certificate(), tls_match_hostname(), and x509_utils_get_dns_names(). Because FreeRDP performs custom Common N… Attack
Exploitation
|
|||||||||
| CVE-2026-67289 | FreeRDPFreeRDP | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isFreeRDP before 3.29.0 (affected versions <= 3.28.0) does not validate CRLF and control characters in the server-controlled RDP redirection TargetNetAddress field. This value is copied into the client's ServerHostname and, when the client co… Attack
Exploitation
|
|||||||||
| CVE-2026-67324 | GitPythongitpython-developers | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isGitPython 3.1.50 fails to recognize joined short-option forms such as -u<value> (the short form of --upload-pack=<value>) when enforcing its default unsafe-option gate. When an application passes attacker-influenced clone options into Repo.… Attack
Exploitation
|
|||||||||
| CVE-2026-67340 | arcadedbArcadeData | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isArcadeDB before 26.7.2 (arcadedb-engine) allows trigger scripts to look up host classes in java.lang.* (via Java.type) because ScriptTriggerExecutor adds java.lang.* to the allowed packages. An authenticated user with UPDATE_SCHEMA permissi… Attack
Exploitation
|
|||||||||
| CVE-2026-67341 | arcadedbArcadeData | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isArcadeDB versions before 26.7.2 fail to enforce scripting authorization checks on the SQL DEFINE FUNCTION statement with LANGUAGE js. Attackers with database access can execute arbitrary JavaScript code by submitting DEFINE FUNCTION stateme… Attack
Exploitation
|
|||||||||
| CVE-2026-67342 | arcadedbArcadeData | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isArcadeDB versions before 26.7.2 contain an authorization bypass vulnerability in HTTP handlers for time series, batch, Prometheus, and Grafana endpoints that fail to validate database access permissions. Attackers can access and modify data… Attack
Exploitation
|
|||||||||
| CVE-2026-8457 | WooCommerce - Social LoginApple | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isThe WooCommerce - Social Login plugin for WordPress is vulnerable to Authentication Bypass in all versions up to and including 2.8.7. This is due to the plugin's Apple login handler accepting the Apple id_token and decoding only its base64 … Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Worth reading quieter, still worth your time
-
Max-severity Exchange server flaw under active exploitation by Kremlin hackers
Russian state hackers are using a maximum-severity vulnerability in Microsoft Outlook’s Exchange Server to backdoor unpatched machines and steal credentials and other confidential information from them, security researchers said Thursday. The attacks are coming from TA488, a tracking name for a group working on behalf of the Kremlin, Proofpoint researchers said Thursday . Proofpoint and the National Security Agency jointly warned last week that the group, also tracked as Laundry Bear and Void Blizzard, had been carrying out similar attacks by exploiting a zero-day vulnerability in an email…
Also in Proofpoint Threat Insight
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.