Monday, August 3, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-
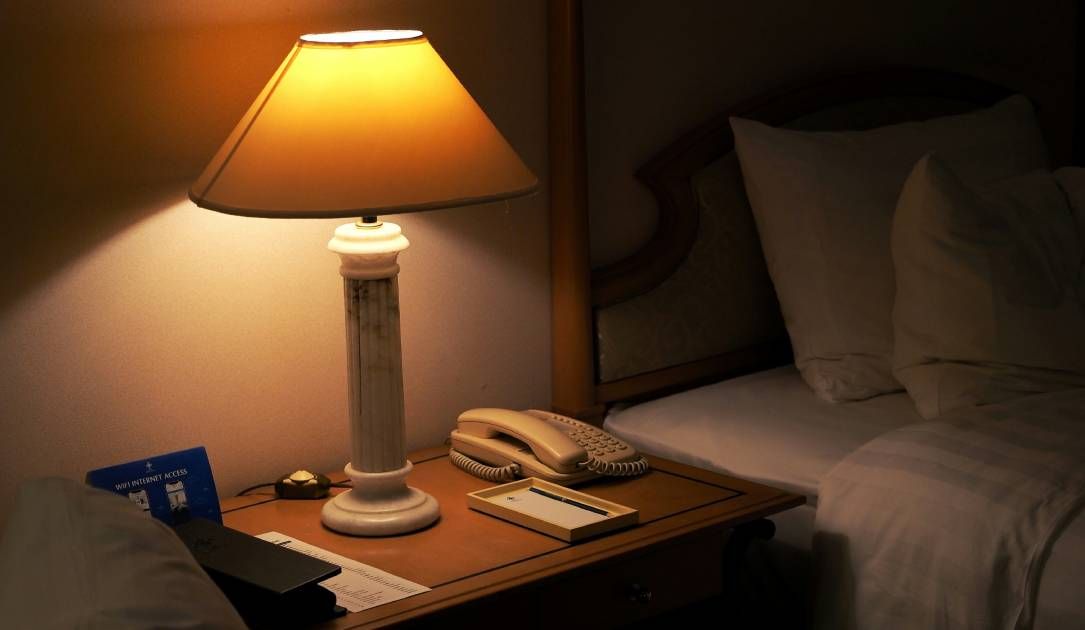
Image: The Record Russian hackers hijack hotel Wi-Fi networks to spy on travelers, Microsoft says
Russian state-sponsored hackers have been compromising hotel Wi-Fi networks around the world to steal travelers' login credentials and infect devices with espionage malware, Microsoft said.
Also in SecurityWeek Malwarebytes Labs The Hacker News
-
Coldcard Hardware Wallet RNG Flaw Linked to $88.6 Million Bitcoin Theft
A firmware flaw in Coldcard hardware wallets has been linked to the theft of approximately $88.6 million in Bitcoin. Attackers exploited a compromised random number generator, allowing them to reconstruct victims’ private keys without ever accessing their devices. Digital asset research firm Galaxy Research first noted unusual activity on July 30, when an attacker drained about 1,082.65 BTC, valued at around $70.2 million, from 1,196 addresses in a rapid sweep lasting just 41 minutes. By August 1, Galaxy detected additional waves of transactions, bringing the total theft to 1,367.05 BTC…
Also in Bleeping Computer The Hacker News

-
MacSync macOS Stealer Uses Fake Claude Guide to Steal Passwords and Crypto Wallets
Mac users searching for Claude installation help have been led into a dangerous trap. A malicious campaign used a paid search result and a fake guide on a legitimate Claude sharing page to persuade victims to paste a command into Terminal. That action started the MacSync information-stealing malware. The campaign shows how software searches can become an entry point for account theft. Rather than exploiting a flaw, the operators relied on trust in a familiar domain, a convincing guide, and a command that looked like an installation step. The result can be stolen browser sessions, passwords…
Also in SANS Internet Storm Center

-
N-able Says Attackers Take Over N-central Servers After Initial Fix Proves Incomplete
N-able said attackers exploited an authentication bypass in N-central to gain remote administrative access and reach the customer systems managed through those servers. Its first fix was incomplete. CVE-2026-18577 affects N-central builds prior to 2026.3.1.7. N-able shipped build 2026.3.1.7 on August 2 as the first unaffected version. N-central is the remote monitoring and management platform
Also in SecurityWeek

-
XCSSET v40 Abuses Chrome DevTools Protocol to Steal Cookies and Run Commands
XCSSET has returned with a way to target macOS developers. The latest version, v40, hides inside poisoned Xcode projects and can turn a local build into a supply-chain compromise. Once activated, it can spread through other projects, raising risk for developers and the organizations that use their code. The malware family was first documented in 2020, but its campaign shows a move toward stealth and scale. It uses memory-based execution, changing payloads, and short-lived files to reduce visible traces. Developers across South Asia have seen heightened targeting, while infected projects have…
Also in Bleeping Computer

-
AI is 'both the weapon and the target' in latest wave of cyberattacks
AI is becoming both an attack tool and a high-value target, with attacks by AI-enabled adversaries rising 89 percent in 2025, according to CrowdStrike. The security firm's annual Threat Hunting Report details criminal gangs and nation states using AI throughout the attack chain. Attackers are also targeting organizations' AI infrastructure and poisoning popular software packages to compromise their users. "AI is both the weapon and the target," CrowdStrike counter adversary division senior VP Adam Meyers told reporters. "AI is a high-value attack surface, and it's being used by more and more…
Also in CyberScoop
-
Cheap Android TV Boxes Pose as Phones and Turn Owners’ Broadband Into Proxies
Bitsight says some cheap Android TV boxes have shipped with apps that rewrite their hardware identity to mimic Samsung, Huawei, Xiaomi, or Vivo phones, then click ads on websites run by the same operators. Researchers named the operation Fuyao and attributed it to Zhejiang Fengwo IoT Technology Co., Ltd., a mainland China company founded in 2019. The same apps have a second job. When a box
Also in Wired Security

-
Adobe Campaign Classic CVSS 10.0 Flaw Could Run Code Without User Interaction
Adobe has released security updates to address a maximum-severity security flaw in Campaign Classic (ACC), its enterprise-focused marketing automation platform, that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-48449, carries a severity score of 10.0 on the CVSS scoring system. It has been described as a case of incorrect authorization that could result in
Also in SecurityWeek

-
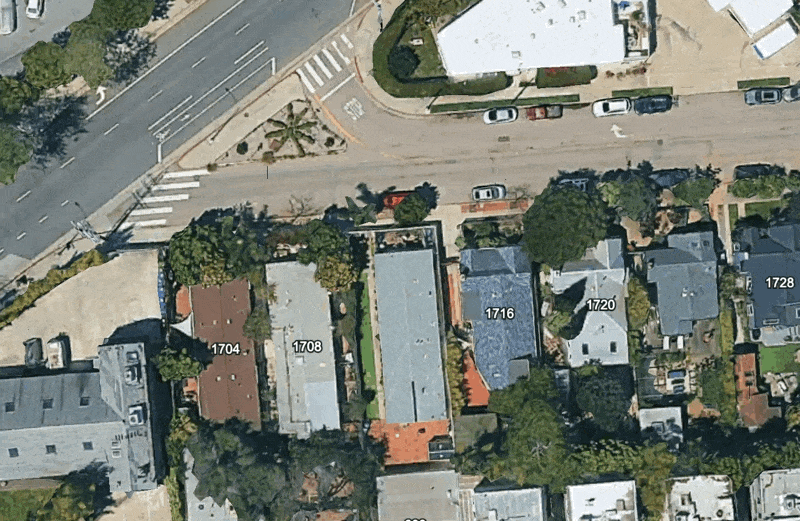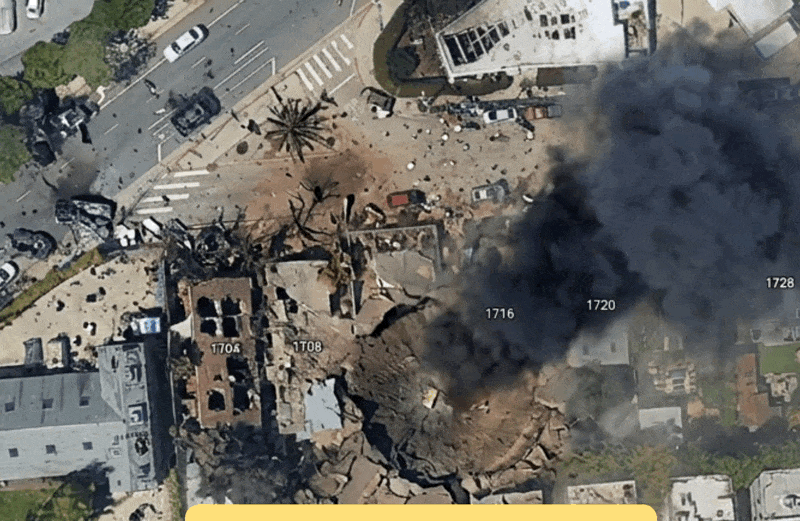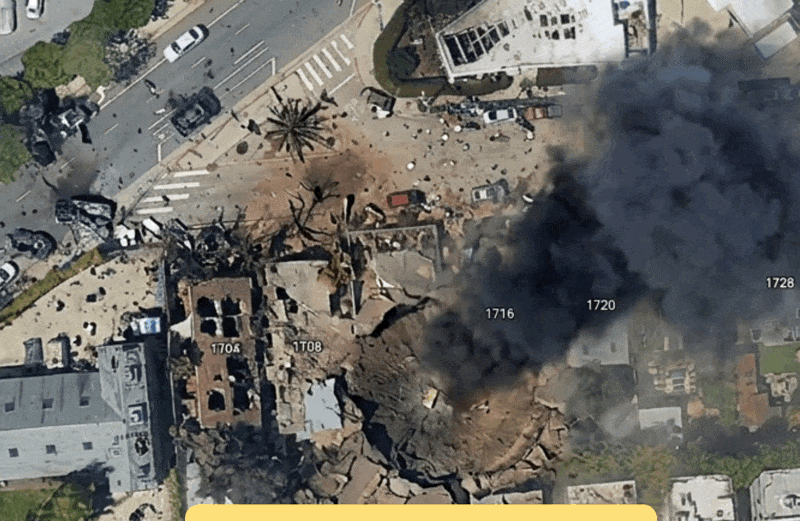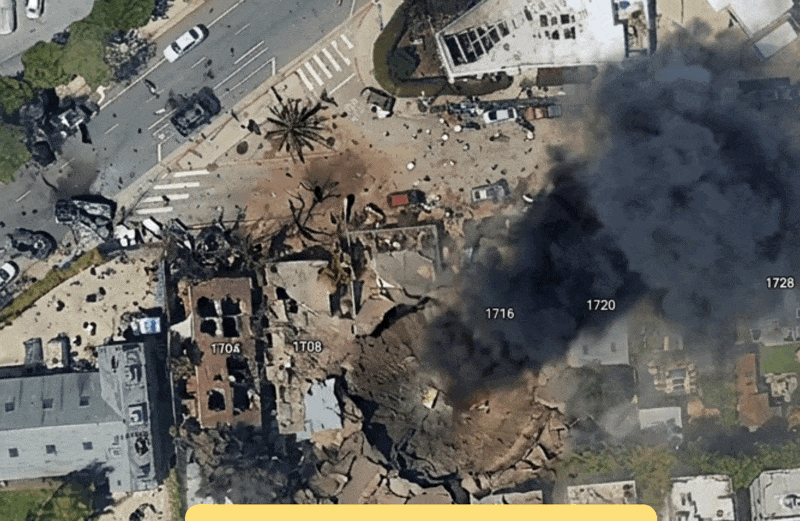
Google Earth’s New AI Lets Anyone Fabricate Completely Bullshit Satellite Images
On Thursday, Google introduced a new AI feature into Google Earth which lets anyone fabricate all sorts of misleading or straight up inaccurate satellite imagery, from making it look like a specific place has suffered a drone strike to manifesting a nuclear plant in Iran. Usually, Google Earth is an exceptionally useful tool for open source intelligence (OSINT) analysts to digitally monitor areas of interest and see how they change over time, say, during a conflict or disaster. Now, Google Earth can easily be used as a tool for disinformation. 💡 Do you work at Google? I would love to hear…
Also in CCCS Alerts & Advisories
Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-65321 | PyAthenalaughingman7743 | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isPyAthena prior to 3.35.4 contains a sql injection vulnerability that allows unauthenticated attackers to inject arbitrary SQL by exploiting improper quote-escaping in DefaultParameterFormatter.format(), which routes DELETE and CTAS statemen… Attack
Exploitation
|
|||||||||
| CVE-2026-68579 | FreeRDPMicrosoft | Critical | 9.6 | — | — | — | — | CVSS 9.6 | |
What it isFreeRDP before 3.30.0 (<= 3.29.0) contains a heap-based buffer overflow in the Windows clipboard client's CliprdrStream_Read function (client/Windows/wf_cliprdr.c). When an OLE paste consumer (e.g. explorer.exe) calls IStream::Read with a f… Attack
Exploitation
|
|||||||||
| CVE-2026-67356 | arcadedbArcadeData | High | 8.8 | — | — | — | — | CVSS 8.8 | |
What it isArcadeDB before 26.7.3 binds the real LocalDatabase object into JavaScript trigger contexts with HostAccess.ALL, allowing schema-admins to call getSecurity().createUser() without permission checks. Attackers with UPDATE_SCHEMA permission ca… Attack
Exploitation
|
|||||||||
| CVE-2025-71399 | better-authbetter-auth | High | 8.6 | — | — | — | — | CVSS 8.6 | |
What it isBetter Auth relies on better-call, which uses the rou3 router library. In affected versions of rou3, paths are normalized by removing empty segments, so /path, //path, and ///path resolve to the same route. In Better Auth versions prior to … Attack
Exploitation
|
|||||||||
| CVE-2026-68581 | vikunjago-vikunja | High | 8.1 | — | — | — | — | CVSS 8.1 | |
What it isVikunja versions 0.22.0 through 2.3.0 fail to validate the principal type in API token management. Because user IDs and link-share IDs are independent numeric sequences and both resolve through a generic web.Auth.GetID() interface, a link-s… Attack
Exploitation
|
|||||||||
| CVE-2026-67357 | arcadedbArcadeData | High | 7.5 | — | — | — | — | CVSS 7.5 | |
What it isArcadeDB versions before 26.7.3 contain an information disclosure vulnerability in the MCP get_server_settings tool that leaks the arcadedb.ha.clusterToken in cleartext. Attackers with MCP access can retrieve the cluster token and use it wi… Attack
Exploitation
|
|||||||||
| CVE-2026-68578 | arcadedbArcadeData | High | 7.5 | — | — | — | — | CVSS 7.5 | |
What it isArcadeDB versions before 26.7.3 fail to bind the authenticated principal in the MCP HTTP transport, causing all engine permission checks to silently pass as no-ops. Non-root MCP-allowed users can perform arbitrary database writes, DDL, sche… Attack
Exploitation
|
|||||||||
| CVE-2026-68580 | FreeRDPFreeRDP | High | 7.5 | — | — | — | — | CVSS 7.5 | |
What it isFreeRDP before 3.29.0 contains integer overflow vulnerabilities in the audio input redirection channel (audin) across ALSA, sndio, WinMM, and OpenSL ES backends that fail to validate the FramesPerPacket parameter from RDP servers. Attackers… Attack
Exploitation
|
|||||||||
| CVE-2026-3245 | PRISMAproductionPalo Alto | High | 7.5 | — | — | — | — | CVSS 7.5 | |
What it isA deserialization vulnerability in PRISMAproduction Version 6.5 or earlier that may lead to arbitrary code execution. Attack
Exploitation
|
|||||||||
| CVE-2025-71400 | passkeybetter-auth | High | 7.1 | — | — | — | — | CVSS 7.1 | |
What it isbetter-auth passkey versions before 1.4.0 contain an insecure direct object reference vulnerability in the passkey deletion endpoint that allows authenticated users to delete arbitrary passkeys by ID. Attackers with valid sessions can submi… Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.