Saturday, August 22, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
- WordPress 1 critical 37
- Unknown 36
- Apache 21
- Combodo 18
- lxc 12 critical 17
- Esri 13
- Microsoft 1 critical 9
- HashiCorp 8
- yootheme.com 6
- j2commerce.com 6
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-

Image: The Hacker News Microsoft Defender's Own Driver Can Be Weaponized to Delete Security Software at Boot
Check Point Research has disclosed a technique that uses Microsoft Defender's own legitimately signed boot-time remediation driver to perform arbitrary kernel-level file and registry operations on Windows systems ranging from Windows 7 through Windows 11 25H2, with no software flaw exploited and no driver imported from outside the machine. The driver, BTR.sys (Boot Time Removal Tool), is a
Also in Bleeping Computer Bleeping Computer Bleeping Computer +3
-
Apple Detected Something on These iPhones | Threat Wire
⬇️ OPEN FOR LINKS TO ARTICLES TO LEARN MORE ⬇️ @endingwithali → Twitch: https://twitch.tv/endingwithali Twitter: https://twitter.com/endingwithali YouTube: https://youtube.com/@endingwithali Everywhere else: https://links.ali.dev Want to work with Ali? hak5@endingwithali.com [❗] Join the Patreon→ https://patreon.com/threatwire 0:00 0 - Intro 1 - Apple’s Threat Notifs 2 - US Hacks Back 3 - Worms R Back 4 - BSides News 5 - Outro LINKS 🔗 Story 1: Apple’s Threat Notifs https://thehackernews.com/2026/08/apple-warns-users-in-110-countries-they.html https://support.apple.com/en-us/102174 🔗 Story 2…
Also in Wired Security CCCS Alerts & Advisories The Register Security

-
Top 10 Best Wireless / Wi-Fi Security Solutions in 2026
Cisco Meraki scores highest in our 2026 evaluation of automatic Wi-Fi security solutions , combining cloud-managed simplicity with strong policy enforcement, while HPE Aruba leads on enterprise-grade wireless security depth, and Juniper Mist wins on AI-driven operations. Wi-Fi security solutions protect wireless networks through encryption (WPA3), authentication (802.1X), rogue access point detection, and client isolation, and in 2026 they increasingly enforce zero-trust policy at the point of connection. Here are the ten best, scored. The 2026 Wi-Fi Security Scorecard Each platform scored…
Also in The Hacker News The Register Security CCCS Alerts & Advisories

-
Android Car Malware Spreads Through Built-In Updaters for Ad Fraud, Proxy Botnet
Cybersecurity researchers have flagged a new malware family that's specifically designed to infect Android-based vehicle head unit firmware developed by DoFun. Kaspersky, which discovered the threat in June 2026, said the end goal of the malware is to serve a multi-stage downloader to enable ad fraud and creation of a proxy botnet. "The malware spread through the built-in updaters of
Also in Kaspersky Securelist The Hacker News The Hacker News +3

-
AWS Security makes an inscrutable choice
One of the best ways to lower your AWS bill by 99 percent or more is by not checking your keys into public GitHub repositories. Many of us have done this inadvertently over the years, and the defenses against it have improved dramatically (my personal favorite being "using non-ephemeral credentials derived from OIDC or SSO is an anti-pattern"), but it still happens. On Friday, BleepingComputer reported on a Truffle Security finding that hundreds of leaked AWS keys are root keys and are somehow still active and valid. AWS Security is full of very smart people who care deeply about a number of…
-
What 45 Million wp2shell Exploit Attempts Reveal About the New Vulnerability Response Window
The latest wp2shell vulnerability was one of the biggest WordPress security events in history. The critical vulnerability chain combined two flaws that allowed unauthenticated attackers to exploit vulnerable sites and ultimately execute malicious code remotely, potentially taking control of them. In the first week after the disclosure, more than 45 million exploit attempts from nearly 150,000 unique network sources were made. And as the volume continued climbing, we saw just how fast vulnerability disclosure can turn into mass exploitation. For comparison, this scale was roughly 20x what was…
Also in Bleeping Computer The Hacker News

-
41 deceptive download sites show a real link, then send you somewhere else
We identified a network of 41 websites impersonating popular games and Windows software, all designed to push visitors towards the same Download Studio installer. The sites advertise everything from Counter-Strike, Half-Life, Fallout, Roblox, PUBG, and The Witcher to VLC, 7-Zip, Paint.NET, VMware, Total Commander, and Foxit PDF. They go to surprising lengths to look convincing, using accurate product information, genuine developer resources, and even real download links. But the link you see isn’t the link you follow. One site promises Counter-Strike. Hover over its download button and the…
Also in Microsoft Security Microsoft Security Microsoft Security +1
-
14 Trojanized npm Packages Drop RedC2 4.0 Linux Backdoor With AI-Assisted C2
Cybersecurity researchers have discovered a set of trojanized npm packages that masquerade as working calendar and streak utilities but are engineered to stealthily deliver an artificial intelligence (AI)-powered Linux implant dubbed RedC2 4.0. "When the module loads, it locates the bundled binary, marks it executable, and launches it as a detached background process," TrendAI, Trend Micro's
Also in Cisco Talos Cisco Talos Infosecurity Magazine

-
AI-Generated Exploit Scripts Target Siemens S7 PLCs in U.S. Critical Infrastructure
The U.S. government on Wednesday warned of an "active threat" targeting critical infrastructure organizations in the country using artificial intelligence (AI)-generated exploit scripts. The activity is targeting Siemens S7 SeriesProgrammable Logic Controllers (PLCs) to conduct reconnaissance and capability development using AI-generated scripts disguised as legitimate monitoring tools. That
Also in Tenable Blog Infosecurity Magazine The Register Security +1

-
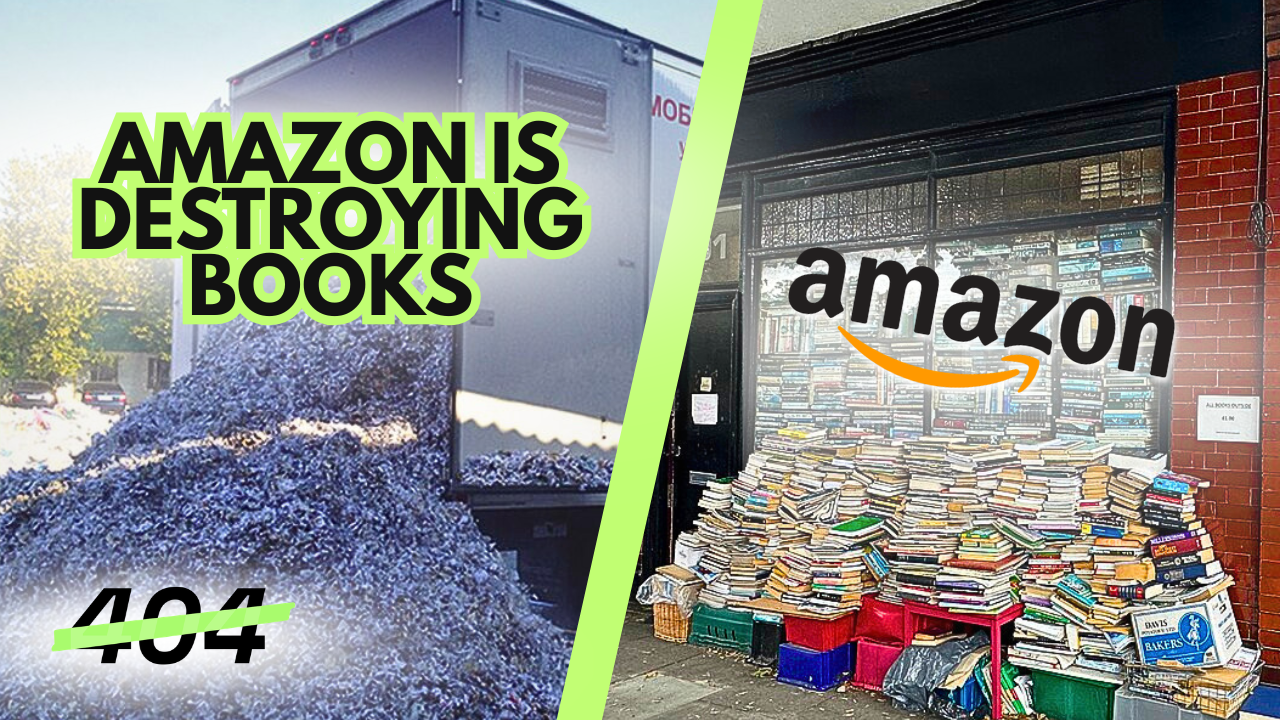
Podcast: Amazon is Destroying Rare Books to Train AI
We start this week with Emanuel’s big story about Amazon buying, and destroying, masses of books to train AI. After the break we talk about a couple of wild cases where people are using AI. In the subscribers-only section, we talk about Meta’s new smart glasses patent and research into how perverts are using them. Listen to the weekly podcast on Apple Podcasts , Spotify , or YouTube . Become a paid subscriber for access to this episode's bonus content and to power our journalism. If you become a paid subscriber, check your inbox for an email from our podcast host Transistor for a link to the…
Also in Bleeping Computer Malwarebytes Labs
Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-69502 | Azure SQL DatabaseMicrosoft | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isServer-side request forgery (ssrf) in Azure SQL Database allows an unauthorized attacker to elevate privileges over a network. Attack
Exploitation
|
|||||||||
| CVE-2026-61539 | inferencexorbitsai | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isXinference is an inference API for running open-source, speech, and multimodal models. In 2.5.0 and earlier, Xinference passes attacker-influenced Llama3 tool-call output to eval() in xinference/model/llm/tool_parsers/llama3_tool_parser.py … Attack
Exploitation
|
|||||||||
| CVE-2026-77683 | CF-N1-SComfast | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA security flaw has been discovered in Comfast CF-N1-S 2.6.0.1. Affected by this issue is the function system of the file /cgi-bin/mbox-config?method=SET§ion=ntp_timezone. The manipulation of the argument timestr results in command inje… Attack
Exploitation
|
|||||||||
| CVE-2026-48749 | incuslxc | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isIncus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image can be used to read or create/write arbitrary files on the host; possibly leading to arbitrary command execution. Version 7.2.0 fixes… Attack
Exploitation
|
|||||||||
| CVE-2026-48750 | incuslxc | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isIncus is a system container and virtual machine manager. Prior to version 7.2.0, the `record-output` parameter of the `/instances/$name/exec` endpoint stores the output of the command in the `exec-output` directory of the instance. If `exec… Attack
Exploitation
|
|||||||||
| CVE-2026-48751 | incuslxc | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isIncus is a system container and virtual machine manager. Prior to version 7.2.0, instance snapshots ignore the `restricted.containers.lowlevel=block` setting; allowing for arbitrary command execution on the Incus server by abusing lowlevel … Attack
Exploitation
|
|||||||||
| CVE-2026-48752 | incuslxc | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isIncus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image or instance backup can be used to read or create/write arbitrary files on the host; possibly leading to arbitrary command execution. … Attack
Exploitation
|
|||||||||
| CVE-2026-48753 | incuslxc | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isIncus is a system container and virtual machine manager. Prior to version 7.1.0, the S3 protocol upload endpoint is vulnerable to path traversal and allows creation of arbitrary files on the host. This behavior could lead to arbitrary comma… Attack
Exploitation
|
|||||||||
| CVE-2026-48755 | incuslxc | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isIncus is a system container and virtual machine manager. Prior to version 7.1.0, improper validation of user-provided backup compression algorithm leads to argument injection in the constructed command line. This leads to an arbitrary file … Attack
Exploitation
|
|||||||||
| CVE-2026-48769 | incuslxc | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isIncus is a system container and virtual machine manager. Prior to version 7.2.0, an arbitrary file write exists in the Incus client when a malicious image server returns a crafted `Incus-Image-Hash` header. This can lead to arbitrary comman… Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.