Thursday, August 27, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
- Unknown 66
- Spring 1 critical 40
- WordPress 1 critical 24
- Dell 1 critical 13
- Apple 8
- WeblateOrg 8
- wintercms 7
- WP Manage Ninja 1 critical 7
- Microsoft 6
- TOOOLS 6
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-

Image: Cyber Security News CISA Warns of Microsoft SQL Server RCE Vulnerability Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency has added a Microsoft SQL Server remote code execution vulnerability , tracked as CVE-2019-1068, to its Known Exploited Vulnerabilities catalog after confirming exploitation in attacks. The flaw affects Microsoft SQL Server and can allow an attacker to execute code under the permissions of the SQL Server Database Engine service account. CVE-2019-1068 is a remote code execution vulnerability in Microsoft SQL Server. Successful exploitation could allow an attacker to run malicious commands on a vulnerable database server, with the level…
Also in CCCS Alerts & Advisories Cyber Security News Bleeping Computer +3
-
Next.js Patches Critical AVIF and Windows Flaws Enabling Unauthenticated RCE
Credit: Hacktron Vercel has released security patches for two critical-severity vulnerabilities in the Next.js web framework, both of which allow unauthenticated remote code execution, one exploitable via specially crafted AVIF image files and the other through a path traversal flaw affecting servers that use a Windows filesystem. The Windows path traversal, tracked as CVE-2026-75604&
Also in Microsoft Security Microsoft Security Microsoft Security +3

-
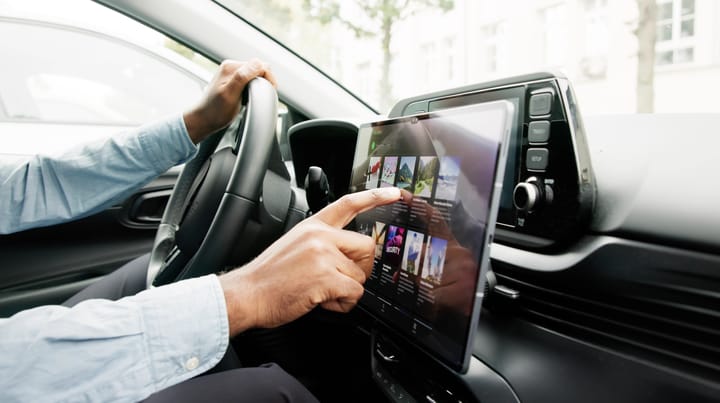
Android Malware Hijacks Update System for Car Head Units
Threat actors behind a notorious click-fraud botnet have set their sights on vehicle infotainment modules and are abusing legitimate functionality to spread infections.
Also in Bleeping Computer Malwarebytes Labs The Hacker News
-
CISA Adds Six Exploited Flaws to KEV, Including NetScaler, Linux, and SQL Server Bugs
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added six flaws to its Known Exploited Vulnerabilities (KEV) catalog, including a high-severity security vulnerability impacting Citrix NetScaler ADC and NetScaler Gateway, citing evidence of active exploitation. The vulnerabilities are listed below - CVE-2019-1068 - A remote code execution vulnerability in
Also in Infosecurity Magazine Bleeping Computer CCCS Alerts & Advisories

-
Learn How to Build Security Operations Ready for AI-Powered Attacks
Security teams have spent years trying to detect threats faster. AI is changing the harder part: how much time defenders have left to act. Advanced AI models can now help attackers discover vulnerabilities, generate exploit code, and move through weaknesses faster than traditional security processes were built to handle. The challenge is no longer just finding another vulnerability or
Also in Microsoft Security Blog Bleeping Computer The Hacker News +2

-
Amazon Kiro Prompt Injection Can Exfiltrate Sensitive Data Through Kiro Powers
Cybersecurity researchers have disclosed details of a vulnerability in Amazon Kiro, an artificial intelligence (AI)-powered, agentic integrated development environment (IDE), that could facilitate data exfiltration via prompt injection and Kiro Powers. The security flaw, which does not have a CVE identifier, works against Kiro IDE 0.7.45 on Windows, according to Mindguard. The latest version of
Also in CyberScoop 404 Media 404 Media

-
Hackers Exploit ownCloud and WordPress Flaws to Steal Philippine Nuclear and Naval Data
A suspected Chinese-speaking operator exploited known ownCloud and WordPress weaknesses to collect sensitive information from a Philippine nuclear research body and a marine engineering company that serves the Philippine Navy. The intrusion shows how unpatched internet-facing systems can expose data with national-security value. The activity came to light after investigators found an openly accessible server containing attack tools, transfer logs, and stolen files. The collection reportedly included reactor-related records, staff data, planning documents, encrypted credential stores, and a…
Also in Bleeping Computer The Hacker News

-
GitLab Fixes Claude AI Agent Flaw That Could Execute Arbitrary Commands in CI Pipeline
GitLab has released security updates to fix a high-severity vulnerability in its Duo Claude AI agent that could allow authenticated developers to execute arbitrary commands within CI pipeline contexts. The flaw, tracked as CVE-2026-18252, affects GitLab Enterprise Edition installations and carries a CVSS score of 7.3. The company issued patched versions GitLab 19.3.1, 19.2.5, and 19.1.7 on August 26, 2026. GitLab strongly urged self-managed customers to update immediately. GitLab.com is already running the corrected software, while GitLab Dedicated customers do not need to take action. The…
Also in Wiz Research

-
ThreatsDay: 296K IoT Botnet, 100+ Water Systems Targeted, SharePoint RCE Chain + 27 New Stories
A fake login page. A fake security scan. A fake productivity app. Apparently, pretending to be useful is still one of the easier ways into a machine. The rest of the week gets stranger: botnets borrowing AI, command traffic hiding in public infrastructure, malicious tools waiting before showing their real behavior, exposed systems getting scanned, and exploit windows shrinking again. Different
Also in Microsoft Security

-
Fake Apple Support AI Calls Target Stolen-Device Owners for Passcodes and 2FA Codes
Cybersecurity researchers have disclosed details of a phishing-as-a-service (PhaaS) platform built to strip Apple's Activation Lock from stolen devices, using rented AI voice agents that call theft victims posing as Apple Support and ask for their device passcode. SOCRadar Threat Research Unit (STRU) said the platform, which it tracks as AnonyMousKIT, is credit-metered and drives lures across
Also in Malwarebytes Labs

Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-60004 | GiteaGitea | Critical | 9.8 | 82% | KEV | — | — | KEVEPSS 82%CVSS 9.8 | |
What it isGitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation. Attack
Exploitation
|
|||||||||
| CVE-2026-32566 | ACPT (Pro) - Custom Post Types Plugin for WordPressWordPress | Critical | 9.8 | 0.4% | — | — | — | EPSS 0.4%CVSS 9.8 | |
What it isUnauthenticated Privilege Escalation in ACPT (Pro) - Custom Post Types Plugin for WordPress <= 2.0.63 versions. Attack
Exploitation
|
|||||||||
| CVE-2026-78286 | Geo ControllerINFINITUM FORM | Critical | 9.8 | 0.5% | — | — | — | EPSS 0.5%CVSS 9.8 | |
What it isUnauthenticated PHP Object Injection in Geo Controller <= 8.9.8 versions. Attack
Exploitation
|
|||||||||
| CVE-2026-78292 | Hash Formhashthemes | Critical | 9.8 | 0.5% | — | — | — | EPSS 0.5%CVSS 9.8 | |
What it isUnauthenticated PHP Object Injection in Hash Form <= 1.4.1 versions. Attack
Exploitation
|
|||||||||
| CVE-2026-74232 | L3_V2_8Zbtlink | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isZbtlink L3_V2_8 firmware 3.0.0.4.528, Zbtlink WE826-T2 firmware 19.1101, Zbtlink ZBT-7628 firmware 1.0.0.2.007, Zbtlink ZBT-ZBT7621 firmware 1.0.0.3.001, MoreQuick MQAC-7620, MQAC-7620A, MQAP-7620, MQAP-7620A, and MQAP-7628 firmware 1.0.0.2… Attack
Exploitation
|
|||||||||
| CVE-2026-74233 | WE1326Zbtlink | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isZbtlink WE1326, WE357, WE5926, WE5926-WD, WE826-Q, WE826-T2, WE826-WD, WG108, and WG3526 firmware 19.1101, Zbtlink WE2426-C firmware 19.1112, Zbtlink WE5926-EC_QP firmware 20.0516, Zbtlink WF3526-P firmware 19.051, CTN720-W1, LF-1541, and M… Attack
Exploitation
|
|||||||||
| CVE-2026-59354 | Spring Security (OAuth2 Authorization Server module)Broadcom | Critical | 9.6 | 0.2% | — | — | — | EPSS 0.2%CVSS 9.6 | |
What it isIn versions of Spring Security's OAuth2 Authorization Server module 7.0.0 through 7.0.4, when Dynamic Client Registration is explicitly enabled, the registration endpoint performs insufficient validation of certain client metadata fields su… Attack
Exploitation
|
|||||||||
| CVE-2026-59270 | Spring SecuritySpring | Critical | 9.4 | 0.3% | — | — | — | EPSS 0.3%CVSS 9.4 | |
What it isSpring Security's embedded UnboundID LDAP server (UnboundIdContainer) unconditionally registers an administrative credential and binds its listener to all available network interfaces. Spring Security 7.1.0 Spring Security 7.0.0 - 7.0.6 Spr… Attack
Exploitation
|
|||||||||
| CVE-2026-32479 | Visitor Traffic Real Time Statistics ProCODEPRESS IT Solutions LLC | Critical | 9.3 | 0.4% | — | — | — | EPSS 0.4%CVSS 9.3 | |
What it isUnauthenticated SQL Injection in Visitor Traffic Real Time Statistics Pro <= 11.17 versions. Attack
Exploitation
|
|||||||||
| CVE-2026-78260 | EpaycoePayco | Critical | 9.3 | 0.4% | — | — | — | EPSS 0.4%CVSS 9.3 | |
Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.