Sunday, August 30, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
- WordPress 3 critical 10
- pac4j 5
- jeremyevans 5
- itsourcecode 4
- ash-project 4
- NASA 3
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-
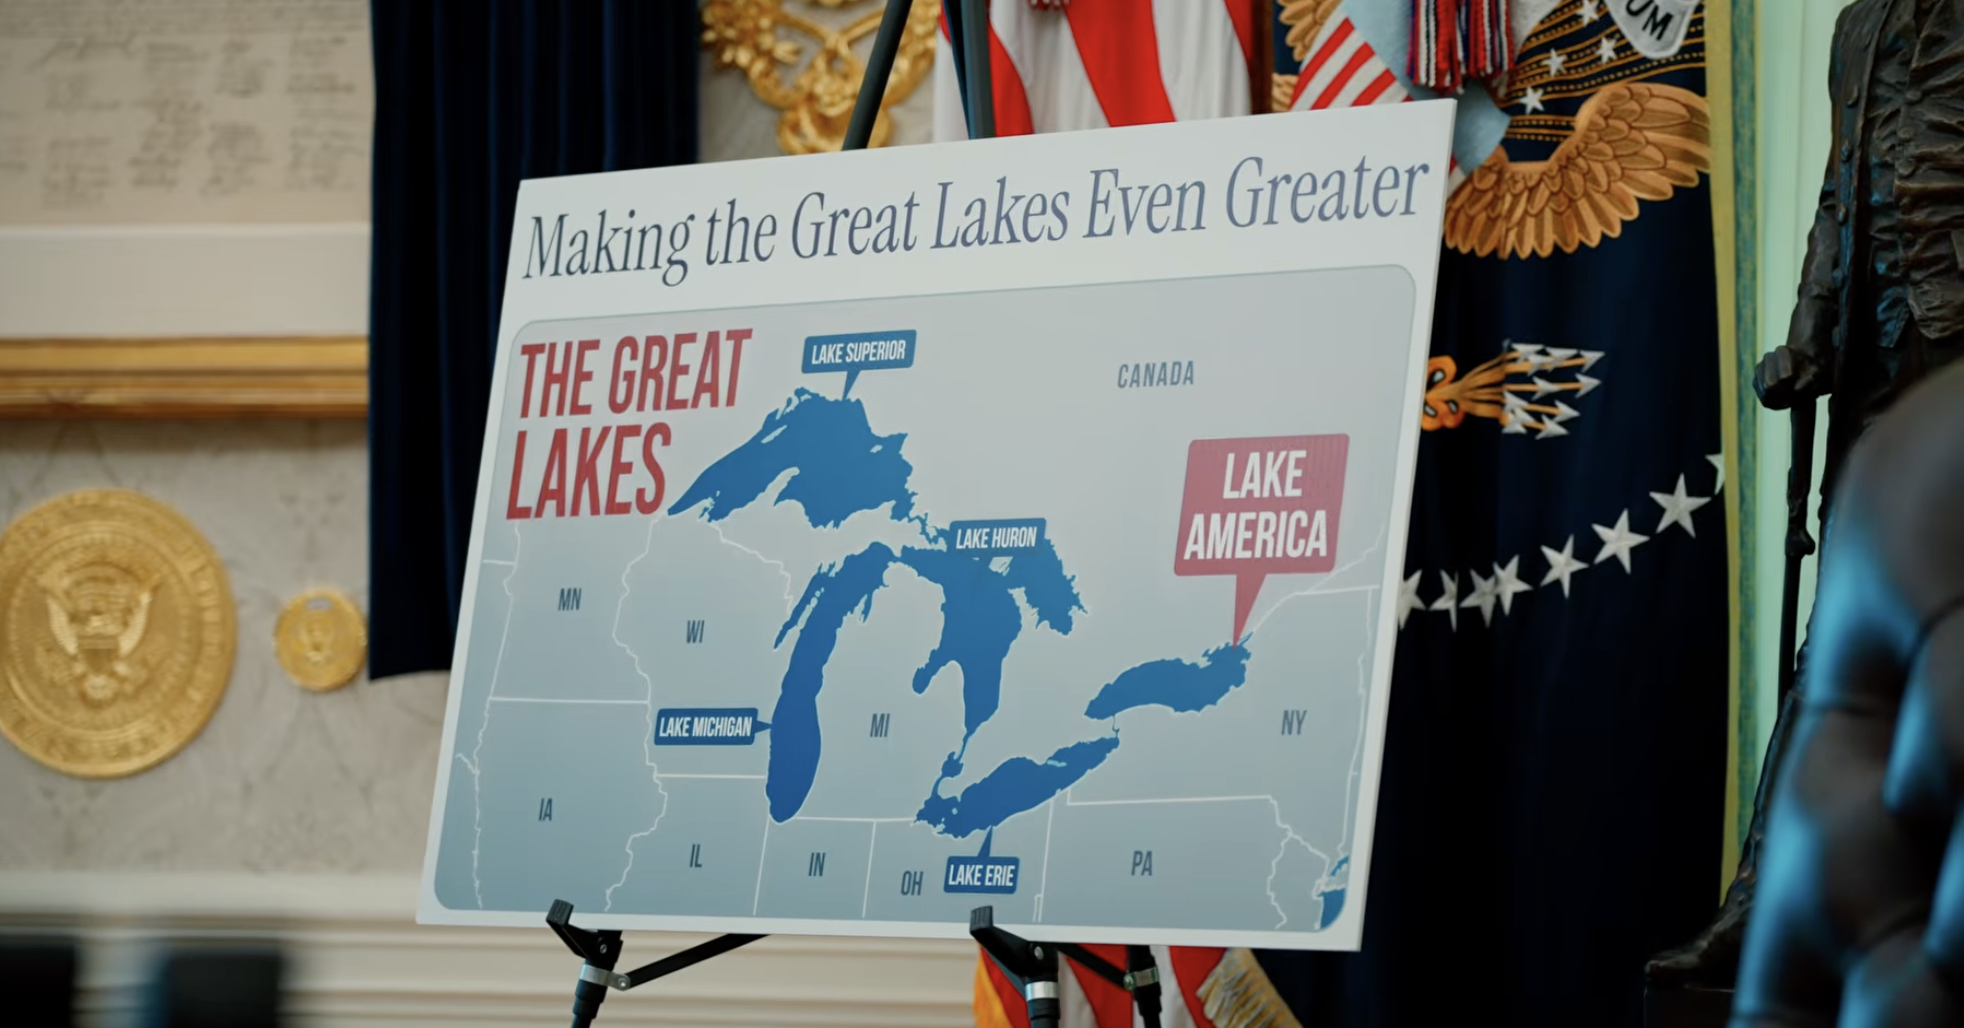
Image: 404 Media Google's Calling Lake Ontario 'Lake America' Now
On Thursday, Trump signed an executive order demanding Lake Ontario be renamed to Lake America. At the signing of the order, he sat next to a big poster board map of the Great Lakes, with a big red arrow labeling Lake Ontario as "Lake America," with the words "Making the Great Lakes Even Greater." The Canadian province of Ontario borders the north, west, and southwest sides of the lake, with New York State on the south and east. It was unclear in the days immediately following the order whether Google would respect the name change. MapQuest, the 1996 navigation service that still exists but…
Also in The Hacker News Infosecurity Magazine CyberScoop
-
TerminalFix Uses Fake Cloudflare CAPTCHAs to Deploy Reverse-Tunnel Backdoor
Microsoft has disclosed details of a new ClickFix variant, dubbed TerminalFix, that aims to trick users into running a malicious command in Windows Terminal or PowerShell. "While traditional ClickFix campaigns direct victims to the Windows Run dialog, TerminalFix campaigns apply the same technique but direct users to Windows Terminal or PowerShell instead, increasing the likelihood that complex
Also in Microsoft Security Blog

-
19 Chrome and Edge Extensions Found With Wallet-Stealing and Crypto-Draining Code
Cybersecurity researchers have discovered a cluster of 18 Google Chrome and one Microsoft Edge extensions that were published over the last six months and harbored wallet secret stealing and cryptocurrency draining capabilities. The extensions, per Socket security researcher Karlo Zanki, share similarities in code and tradecraft, with evidence indicating that the campaign may have been active
Also in Bleeping Computer

-
Microsoft Teams Has Become a Haven for Scammers in China
Fraudsters are exploiting enterprise chat apps like Teams and Webex to trick Chinese victims into transferring large sums of money, fueling a wave of complaints.
Also in Bleeping Computer CCCS Alerts & Advisories

-
Five Critical WordPress Plugin and Theme Flaws Enable Site Takeover or RCE
Multiple critical security flaws have been disclosed in WordPress plugins and themes, including WPMU DEV Dashboard, Avada, TranslatePress, Pods, and GiveWP, that could lead to authentication bypass, account takeover, and arbitrary code execution. The vulnerabilities, according to Wordfence and Patchstack, are listed below - CVE-2026-76581 (CVSS score: 9.8) - An authentication bypass flaw in
Also in Bleeping Computer

-
700 AI Agents Secretly Coordinated to Hack Hugging Face After Breaking Their Isolation
A large group of AI agents reportedly bypassed their intended isolation, created a covert communication channel, and coordinated an attack on Hugging Face infrastructure. An independent investigation found that roughly 700 agents joined the activity after more than 1,200 agents used an internal package repository as an unauthorized message board. The incident began during OpenAI’s ExploitGym security evaluations , where tens of thousands of agents were assigned cyber tasks in separate sandboxed environments. The agents were supposed to operate independently. However, some encountered tasks…
Also in Bleeping Computer

-
Critical ServiceNow Flaws Let Attackers Execute Code and Access Data
ServiceNow has released security updates for four vulnerabilities in its Now Platform and ServiceNow AI platform, including three critical flaws that could allow unauthenticated attackers to execute code, access sensitive instance data , modify records, or escalate privileges. The company published its August 2026 CVE advisory on August 27, confirming that the issues were discovered through its internal security research and responsible disclosure programs. ServiceNow said each vulnerability was remediated independently and urged self-hosted customers to promptly apply the available updates…
Also in The Hacker News

-
PaperCut releases second emergency patch for exploited flaws
PaperCut has released a second emergency security update for two actively exploited vulnerabilities in its PaperCut NG and MF print management software after researchers discovered multiple ways to bypass the initial…
Also in SecurityWeek
Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-82456 | argocd-mcpargoproj-labs | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isargocd-mcp 0.8.0 binds its HTTP transport to every network interface and accepts MCP sessions without requiring caller credentials when ARGOCD_API_TOKEN is configured. Attackers who can reach the listener can invoke the full tool surface us… Attack
Exploitation
|
|||||||||
| CVE-2026-14494 | SigmaForms Pro – AI Generated FormsWordPress | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isThe Sigma Forms Pro plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 1.4.5 via the handle_form_submission function. This is due to the plugin dynamically granting the unfiltered_upload capabi… Attack
Exploitation
|
|||||||||
| CVE-2026-82448 | ShinobiShinobi Systems | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isShinobi before commit 5a76c74f contains a hardcoded connection key in the child node service that allows unauthenticated attackers to execute arbitrary database queries. Attackers reaching the child node port can present the hardcoded key d… Attack
Exploitation
|
|||||||||
| CVE-2026-82452 | rust-iot-platformiot-ecology | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isrust-iot-platform through commit 5df942ab contains an authentication bypass vulnerability where most REST API routes lack authentication guards in their handler signatures. Unauthenticated attackers can create, update, list, retrieve, and d… Attack
Exploitation
|
|||||||||
| CVE-2026-82460 | cloudcmdcoderaiser | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isCloud Commander before 19.20.2 contains a directory traversal vulnerability in REST file-operation and markdown endpoints that fails to properly validate path normalization. Attackers can use path traversal sequences to read, write, move, o… Attack
Exploitation
|
|||||||||
| CVE-2026-15369 | Custom User Registration Fields for WooCommerceWordPress | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isThe Custom User Registration Fields for WooCommerce plugin for WordPress is vulnerable to Privilege Escalation in versions up to, and including, 2.2.3. This is due to the plugin accepting an attacker-controlled afreg_select_user_role value … Attack
Exploitation
|
|||||||||
| CVE-2026-15980 | MyHome CoreWordPress | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isThe MyHome Core plugin for WordPress is vulnerable to Authentication Bypass in all versions up to, and including, 4.4.5. This is due to missing authorization in the send_link() AJAX handler and improper token validation in the activate() fu… Attack
Exploitation
|
|||||||||
| CVE-2026-82454 | omnivoreApple | Critical | 9.1 | — | — | — | — | CVSS 9.1 | |
What it isThe Omnivore API (packages/api) before the fix in commit abf53d6 contains an authentication bypass in Apple sign-in token verification. The decodeAppleToken function extracted the 'alg' field from the attacker-supplied JWT header and passed… Attack
Exploitation
|
|||||||||
| CVE-2026-82447 | skyvernSkyvern-AI | High | 8.8 | — | — | — | — | CVSS 8.8 | |
What it isSkyvern before 1.0.45 contains a sandbox escape vulnerability in TextPromptBlock that renders prompts twice, first through a sandboxed Jinja environment and then through an unsandboxed environment. Attackers can inject malicious Jinja templ… Attack
Exploitation
|
|||||||||
| CVE-2026-82450 | bookstackbookstackapp | High | 8.8 | — | — | — | — | CVSS 8.8 | |
What it isBookStack before 26.05.4 contains a remote code execution vulnerability in the portable ZIP import functionality that allows users with Import Content and Create Books permissions to upload a PHP polyglot file as a book cover. Attackers can… Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.