Monday, August 31, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
- ash-project 25
- Unknown 25
- D-Link 6 critical 8
- Apache 8
- itsourcecode 7
- nodemailer 1 critical 7
- ToolJet 3 critical 7
- Linux Foundation 6
- WWBN 6
- hulumi 4 critical 6
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-

Image: The Hacker News TerminalFix Uses Fake Cloudflare CAPTCHAs to Deploy Reverse-Tunnel Backdoor
Microsoft has disclosed details of a new ClickFix variant, dubbed TerminalFix, that aims to trick users into running a malicious command in Windows Terminal or PowerShell. "While traditional ClickFix campaigns direct victims to the Windows Run dialog, TerminalFix campaigns apply the same technique but direct users to Windows Terminal or PowerShell instead, increasing the likelihood that complex
Also in Bleeping Computer Microsoft Security Blog
-
Security Risk Advisors Launches SCALR AI as a Free SOC AI Platform for Security Teams
Philadelphia, Pennsylvania, United States, August 24th, 2026, CyberNewswire Security Risk Advisors (SRA) , the authors of the free VECTR platform, announce today another great free platform launch: SCALR AI. Security teams can get SCALR AI for free, delivered through the Azure Marketplace. SCALR AI is an agentive workbench that automates time-consuming security work and ships with fully functional incident triage and enrichment, with AI-driven quality review built-in. There are no limits on the free license (such as local use), and the SCALR AI platform is available to CISO teams to deploy in…
Also in SecurityWeek The Hacker News

-
Hackers Hide ValleyRAT Backdoor Inside Adware Targeting Users in China and India
Hackers are using adware to deliver ValleyRAT, a Windows backdoor. The campaign primarily affects users in China and India, turning a program expected to display ads into a route for spying, theft, and further malware delivery. The installer changes its visible behavior according to its filename. One version installs a collaboration app, another installs a browser, and a third opens a meeting-download page. Those harmless-looking actions can keep a victim occupied while the malicious components are placed on the machine. Researchers at Securelist identified the activity after an apparent…
Also in Microsoft Security Microsoft Security Microsoft Security

-
Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams
Learn how the Spring Ring campaign abuses Microsoft Teams and voice phishing to deploy malware and target enterprise domain controllers.
Also in Bleeping Computer Bleeping Computer
-
Microsoft Investigating New Exchange Online Outage Tracked as EX1464935 [Updated]
Microsoft has opened an active investigation into a new Exchange Online disruption after a wave of user reports flagged access and mail-flow problems across the cloud-based email service. The incident, logged in the Microsoft 365 admin center as EX1464935, began at 9:23 PM IST on August 31, 2026, with the company confirming at 9:25 PM IST that engineers were “investigating user reports of Exchange Online issues”. As of the latest update, the status remains listed as “Investigating,” meaning Microsoft has not yet isolated a root cause or confirmed the scope of the disruption. The advisory…
Also in Bleeping Computer

-
HardBreacher PoC Claims Kaspersky Endpoint 0-Day Privilege Escalation on Windows 11
HardBreacher’s newly published PoC claims a local privilege-escalation flaw in Kaspersky Endpoint Security on fully patched Windows 11 systems, but the issue remains unverified and has not been publicly confirmed or assigned a CVE by Kaspersky. The project, published by a researcher, MSNightmare, describes the alleged flaw as a zero-day elevation-of-privilege vulnerability in Kaspersky’s enterprise endpoint product. According to the repository’s README, the proof of concept was tested on Windows 11 version 25H2 with Kaspersky Endpoint Security version 14.0.0.504. HardBreacher appears to…
Also in SecurityWeek

-
China-Linked Fire Ant Hijacks Cisco Routers to Steal Credentials and Blind Security Logs
A China-nexus cyber espionage actor tracked as Fire Ant has expanded a long-running campaign beyond VMware hypervisors to compromise Cisco IOS XR routers, Terminal Access Controller Access-Control System (TACACS) servers, and Linux management hosts used to route, authenticate, and manage high-value networks. Sygnia, the incident response firm that investigated the intrusion, said the actor
Also in Bleeping Computer

-
Anthropic warns infostealer malware is hijacking Claude sessions to drain usage
Anthropic is warning some Claude users that infostealer malware on their PCs has stolen active Claude login sessions, allowing attackers to access accounts and consume their usage.
Also in SecurityWeek
-
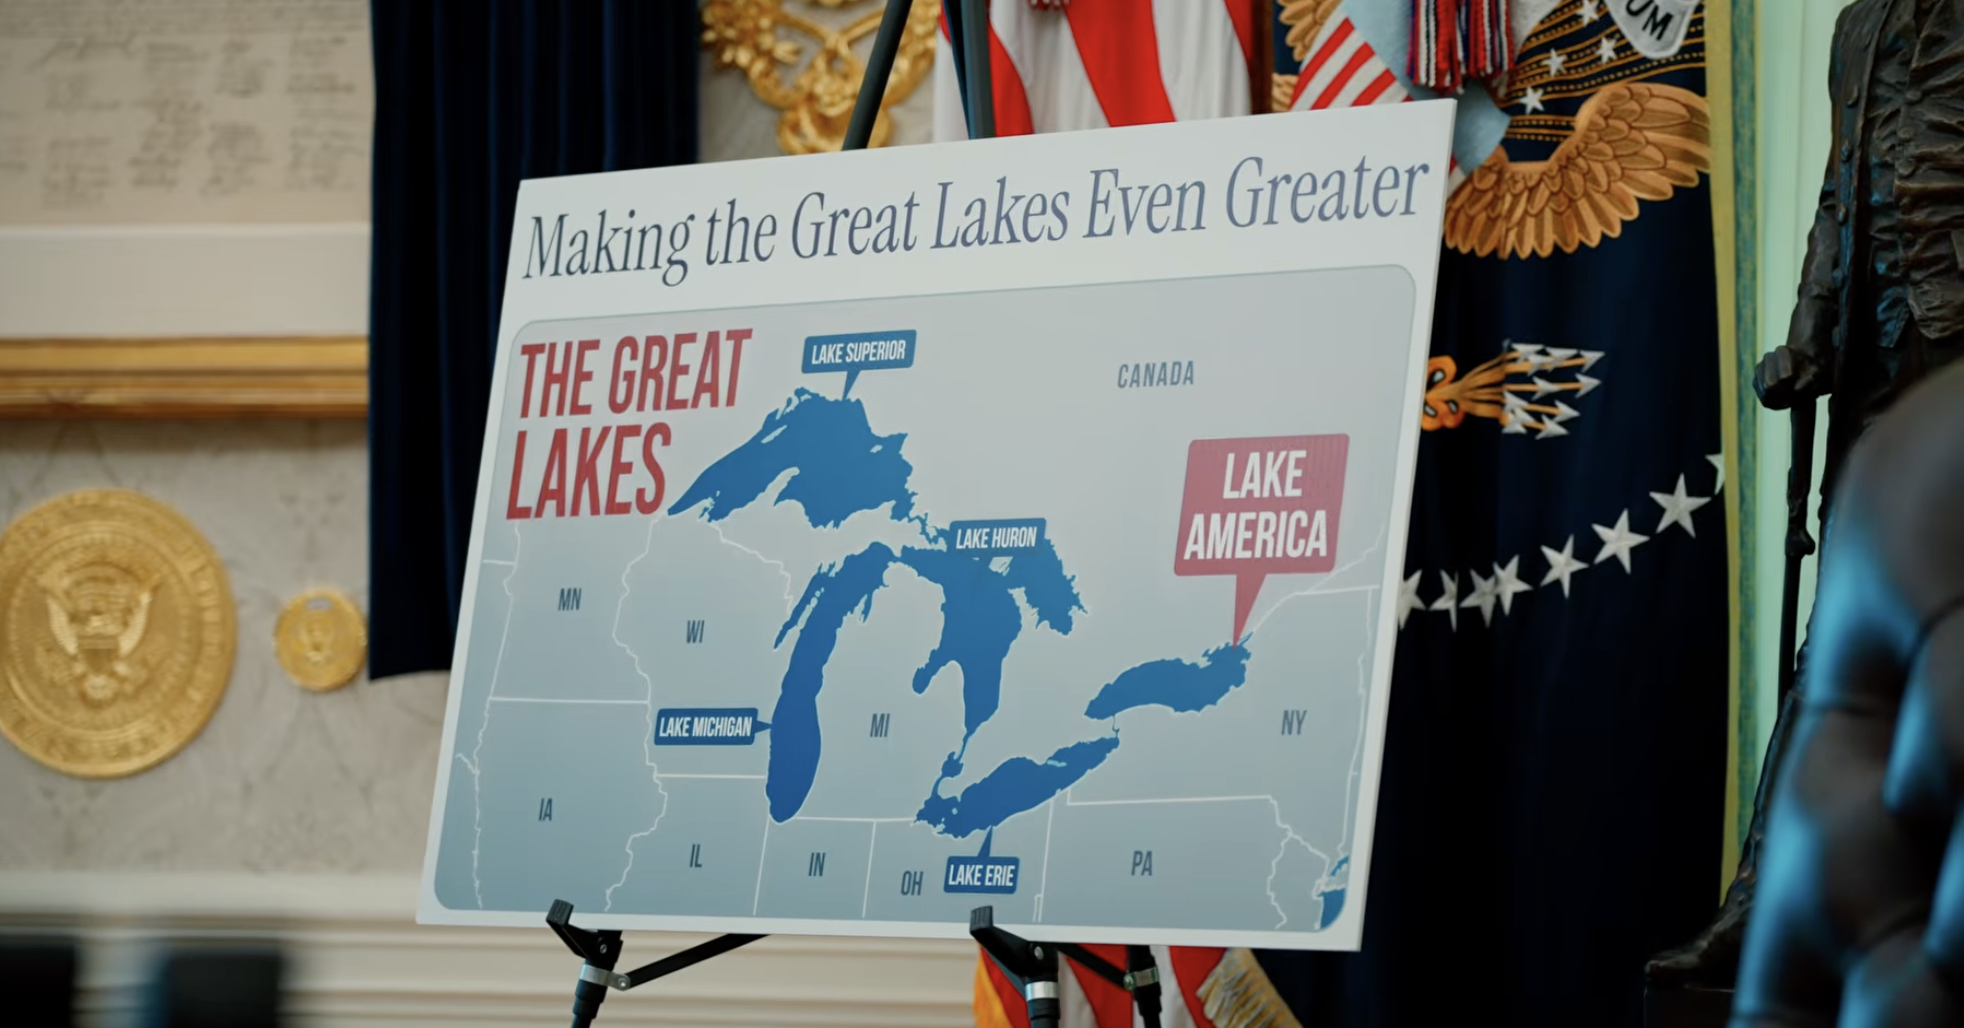
Google's Calling Lake Ontario 'Lake America' Now
On Thursday, Trump signed an executive order demanding Lake Ontario be renamed to Lake America. At the signing of the order, he sat next to a big poster board map of the Great Lakes, with a big red arrow labeling Lake Ontario as "Lake America," with the words "Making the Great Lakes Even Greater." The Canadian province of Ontario borders the north, west, and southwest sides of the lake, with New York State on the south and east.
Also in Bleeping Computer
Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-82542 | HG10Tenda | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isA weakness has been identified in Tenda HG10 300001138. Affected by this issue is the function formIPv6Routing of the file /boaform/admin/formIPv6Routing of the component Boa Web Server. This manipulation of the argument destNet causes buff… Attack
Exploitation
|
|||||||||
| CVE-2026-82592 | DIR-825MD-Link | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA vulnerability was detected in D-Link DIR-825M 1.1.8. This affects the function sub_46725C of the file /boafrm/formDiskFormat of the component Disk Formatting Handler Endpoint. The manipulation of the argument partition results in stack-ba… Attack
Exploitation
|
|||||||||
| CVE-2026-82593 | DIR-825MD-Link | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA flaw has been found in D-Link DIR-825M 1.1.8. This impacts the function sub_41802C of the file /boafrm/formLtefotaUpgradeFibocom of the component LTE Module Firmware Upgrade. This manipulation of the argument fota_url causes stack-based b… Attack
Exploitation
|
|||||||||
| CVE-2026-82616 | NR1800XTOTOLINK | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA vulnerability was found in TOTOLINK NR1800X 9.1.0u.6681_B20230703. Impacted is the function setUploadSetting of the file /cgi-bin/cstecgi.cgi. The manipulation of the argument FileName results in stack-based buffer overflow. The attack ca… Attack
Exploitation
|
|||||||||
| CVE-2026-82874 | ToolJetToolJet | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isToolJet before v3.16.208 fails to validate that authenticated users belong to the organization specified in the organizationId path parameter of tooljet-db endpoints, allowing any Builder user to read, modify, and delete tables across tenan… Attack
Exploitation
|
|||||||||
| CVE-2026-82689 | DNS-320LD-Link | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA vulnerability was detected in D-Link DNS-320L, DNS-327L, DNS-340L and DNS-345 up to 20260717. Affected is an unknown function of the file /cgi-bin/isomount_mgr.cgi of the component ISO Image Handler. The manipulation of the argument upIso… Attack
Exploitation
|
|||||||||
| CVE-2026-58574 | PowerStore 500TDell | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isDell PowerStore contains a Missing Authentication for Critical Function vulnerability. An unauthenticated attacker with network access to the restricted management interface could potentially exploit this vulnerability to read internal syst… Attack
Exploitation
|
|||||||||
| CVE-2026-82854 | nodemailernodemailer | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isNodemailer before 8.0.4 is vulnerable to SMTP command injection through the unsanitized envelope.size parameter. When an application passes a custom envelope object with a size property containing CRLF characters to sendMail(), the value is… Attack
Exploitation
|
|||||||||
| CVE-2026-82855 | policieshulumi | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it is@hulumi/policies versions before 1.3.2 contain an evidence validation bypass vulnerability in Cloudflare and deployment-governance validators that allows attackers to suppress violations by submitting unrelated compliant evidence. Attackers… Attack
Exploitation
|
|||||||||
| CVE-2026-82856 | policieshulumi | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it is@hulumi/policies versions before 1.3.2 fail to properly validate set-qualified AWS IAM condition operators in GitHub OIDC trust policies. Attackers can use ForAnyValue:StringLike operators to hide wildcard GitHub Actions OIDC subject condit… Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.