Monday, September 14, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
- Contec Co., Ltd. 1 critical 32
- Samsung 20
- Unknown 19
- Mattermost 10
- D-Link 6 critical 9
- regularlabs.com 9
- SourceCodester 8
- Simon Tatham 7
- Apache 7
- WordPress 1 critical 6
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-
Image: The Register Security Perfect-10 GitLab bug under attack days after patch lands
CISA says attackers are exploiting a maximum-severity GitLab flaw that lets unauthenticated miscreants read arbitrary files from vulnerable servers after the code shack released fixes on September 10. The US Cybersecurity and Infrastructure Security Agency has added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog. The vulnerability is a path traversal bug in the repository commits API affecting GitLab Community Edition and Enterprise Edition. GitLab rates it a perfect 10.0, the maximum score on the CVSS v3.1 severity scale. Under certain conditions, an attacker doesn't need to…
Also in Rapid7 Blog Infosecurity Magazine Bleeping Computer +2
-
Microsoft Offers Up to $30,000 for Critical AI Flaws in Dynamics 365 and Power Platform
Microsoft is offering security researchers up to $30,000 for finding critical AI vulnerabilities in Dynamics 365 and Power Platform, sharpening its focus on flaws that could manipulate AI inference or expose information through model behavior. The program covers qualifying bugs in Microsoft-hosted services and third-party or open-source components embedded in them, provided researchers demonstrate a security impact on an in-scope service. Under the bounty table, a high-quality report documenting critical “Inference Manipulation” or “Inferential Information Disclosure” can earn the maximum…
Also in Schneier on Security Bleeping Computer Bleeping Computer +1

-
A week in security (September 7 – September 13)
Here’s what we’ve covered in the last seven days on Malwarebytes Labs: Crypto customers targeted by scammers after email marketing provider breach Android malware creates a hidden copy of your banking app BlueMoon exploit kit turns Chrome and Windows flaws into attacks Will AI kill us all within the next decade? Update Chrome now to protect against an actively exploited vulnerability Copyright scammers get Instagram accounts suspended and demand payment More than 100,000 fake stores are out to steal your card details Microsoft fixes record 964 flaws, including 2 exploited zero-days The push…
Also in CCCS Alerts & Advisories Bleeping Computer
-
Cyclops Blink Evolves Into x86-64 Linux Implant With Packet Sniffing and Internal Network Scanning
Cyclops Blink has returned in a form that gives attackers a deeper view inside corporate networks. The malware was found on compromised Cisco Firewall Management Center devices, where it can maintain remote access, inspect traffic, and map systems behind the network edge. The activity is concerning because management appliances occupy trusted positions. Recent reporting that covered attackers gaining root access shows how a breach at this layer can expose configurations, credentials, and paths to systems that are otherwise difficult to reach. Analysts at Sophos identified the new implant in…
Also in Cyber Security News Zero Day Initiative Zero Day Initiative +2
-
Hackers exploit Tencent app flaw to deploy GrayRabbit malware
Threat actors linked to a China-aligned espionage group are exploiting a critical vulnerability (CVE-2026-51990) in Tencent's Sogou Input Method for Windows to deploy the GrayRabbit backdoor.
-
Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware
A single X DM split into two malware chains: AMOS stealer on Mac, NetSupport Manager on Windows, see the Huntress SOC analyst breakdown.
Also in Malwarebytes Labs
-
Malicious Twitch Extension Exposes OAuth Tokens of 30,000 Chrome and Firefox Users
A browser extension promoted as a Twitch viewing helper has been found sending live account tokens through servers controlled by its operator. The add-on, called “Twitch Enhanced Viewer | JeetBot,” was available to Chrome and Firefox users and advertised conveniences such as ad blocking, higher-quality playback, region-unlocked streams, and automatic channel-point collection. The risk sits behind those seemingly useful features. To alter video delivery, the extension reroutes Twitch playlist requests through third-party proxies. During that process, it captures the logged-in user’s OAuth…
Also in Infosecurity Magazine The Hacker News

-
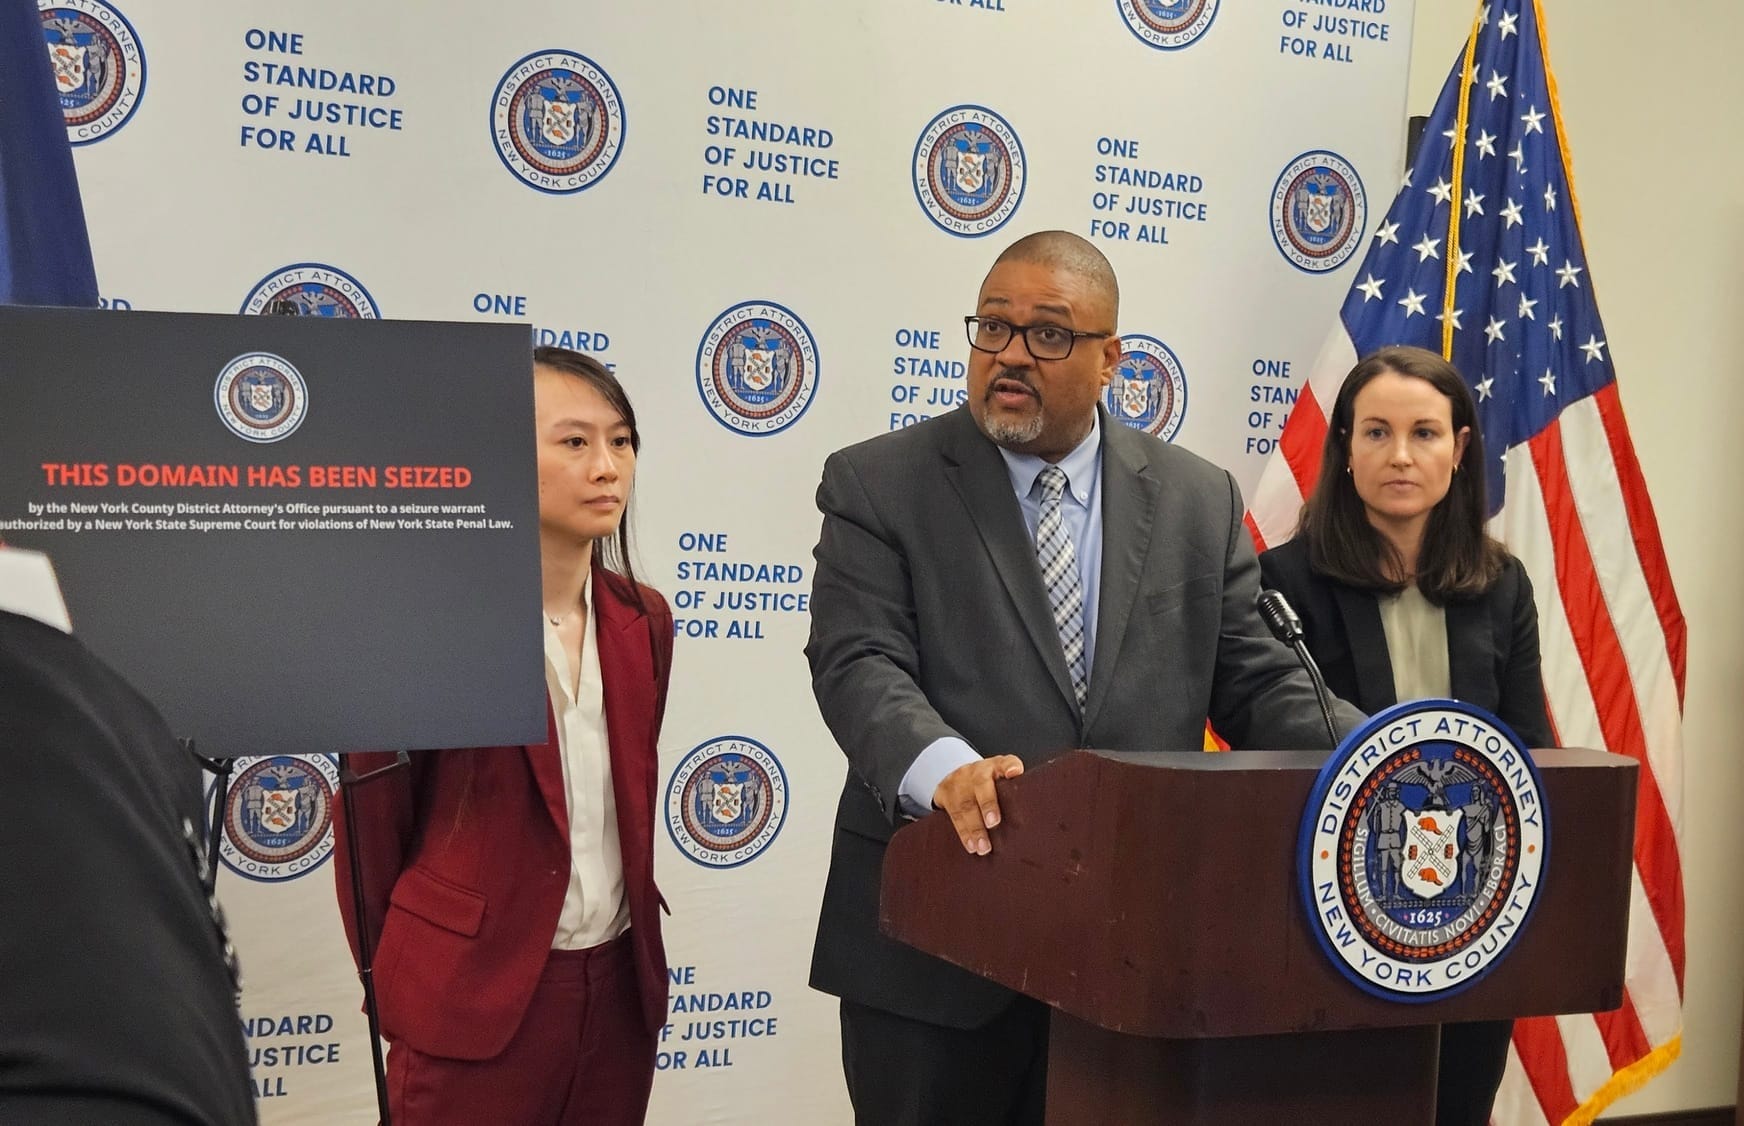
New York Seizes 12 Celebrity Deepfake Websites
The New York District Attorney announced on Monday that it has seized 12 websites hosting AI-generated non-consensual intimate imagery, primarily of celebrities and public figures. The DA’s office said it believes that this marks the largest seizure of such sites in history. The people using and running these sites who are now under investigation used AI tools to turn approximately 1,200 people’s photos into “hyper-realistic” images and videos of them engaged in sexual conduct, according to the DA’s office. The images allegedly depicted “politicians, first ladies of multiple countries…
Also in Wired Security
-
Hackers Mass-Scan Exposed Vite Servers to Steal AWS and Azure Cloud Credentials
Hackers are conducting a large-scale automated scanning campaign against internet-exposed Vite development servers, attempting to steal AWS credentials , Azure access tokens, environment variables, and Infrastructure-as-Code secrets. F5 honeypot sensors recorded 807 session-grouped attacks and about 32,000 raw events in August 2026, a sharp increase from only 1,732 Vite-related file-read events observed over the previous three months. The operation primarily exploited CVE-2026-39364, a high-severity Vite file-disclosure vulnerability published in April 2026. Attackers also tested older Vite…
Also in Bleeping Computer Cyber Security News

-
Revolut discloses data breach exposing financial info, passports
Fintech company Revolut has disclosed a data breach after sharing data from an undisclosed number of customers with a threat actor impersonating a government agency.
Also in SecurityWeek

Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-81648 | CryptoPayment GatewayWordPress | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isThe CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of its AJAX endpoints, allowing unauthenticated users to invoke administrative operations, including deleting arbitrary files on the… Attack
Exploitation
|
|||||||||
| CVE-2026-90605 | A3002MUTotolink | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA weakness has been identified in Totolink A3002MU Hh-B20211125.1046. This vulnerability affects the function formFilter of the file /boafrm/formFilter of the component boa. Executing a manipulation of the argument ip6addr can lead to buffe… Attack
Exploitation
|
|||||||||
| CVE-2026-90606 | A3002MUTotolink | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA security vulnerability has been detected in Totolink A3002MU Hh-B20211125.1046. This issue affects the function formIpv6Setup of the file /boafrm/formIpv6Setup of the component boa. The manipulation of the argument static_ipv6 leads to bu… Attack
Exploitation
|
|||||||||
| CVE-2026-90607 | A3002MUTotolink | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA vulnerability was detected in Totolink A3002MU Hh-B20211125.1046. Impacted is the function formNewSchedule of the file /boafrm/formNewSchedule of the component boa. The manipulation of the argument submit-url results in buffer overflow. T… Attack
Exploitation
|
|||||||||
| CVE-2026-90608 | A3002MUTotolink | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA flaw has been found in Totolink A3002MU Hh-B20211125.1046. The affected element is the function formPortFw of the file /boafrm/formPortFw of the component boa. This manipulation of the argument service_type causes buffer overflow. It is p… Attack
Exploitation
|
|||||||||
| CVE-2026-90680 | DIR-823GD-Link | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA security flaw has been discovered in D-Link DIR-823G 1.0.2B05_20181207. The impacted element is the function strcpy of the file /HNAP1/SetStaticRouteSettings of the component HNAP1. The manipulation of the argument PAddress/SubnetMask/Gat… Attack
Exploitation
|
|||||||||
| CVE-2026-90692 | DIR-878D-Link | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA vulnerability was detected in D-Link DIR-878 120B05. This affects the function SetDynamicDNSIPv6Settings of the component Dynamic DNS IPv6 Settings. The manipulation of the argument IPv6Address/Hostname results in stack-based buffer overf… Attack
Exploitation
|
|||||||||
| CVE-2026-90693 | DIR-878D-Link | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA flaw has been found in D-Link DIR-878 120B05. This impacts the function SetWan3Settings of the component WAN Settings. This manipulation of the argument Primary/Secondary causes stack-based buffer overflow. Remote exploitation of the atta… Attack
Exploitation
|
|||||||||
| CVE-2026-90699 | DWR-M920D-Link | Critical | 9.9 | — | — | — | — | CVSS 9.9 | |
What it isA weakness has been identified in D-Link DWR-M920 1.1.7. This issue affects the function sub_41E60C of the file /boafrm/formPinManageSetup. This manipulation of the argument newPin causes os command injection. The attack can be initiated re… Attack
Exploitation
|
|||||||||
| CVE-2026-82787 | CPSL-08P1ENContec Co., Ltd. | Critical | 9.8 | — | — | — | — | CVSS 9.8 | |
What it isMissing authentication for critical function vulnerability exists in CPSL-08P1EN. If this vulnerability is exploited, an affected product may be operated by a remote attacker without authentication. Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.