Friday, September 18, 2026 · generated · about 6 min read
Morning Brief
Patch today vendors with the most new CVEs today
- Linux 551
- WordPress 81
- Apple 1 critical 40
- Microsoft 13 critical 39
- Dell 24
- patriksimek 14 critical 24
- Google 19
- Synology 2 critical 19
- Unknown 17
- Red Hat 15
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-

Image: Cyber Security News Android Apps Can Now Check If Your Phone Is Missing Critical Security Patches
Android has released new Security State libraries that allow apps and enterprise tools to check whether a device is missing important security patches. The update gives developers a more detailed view of Android security than the traditional monthly Security Patch Level , helping apps identify unpatched system components, pending updates, and specific vulnerability fixes. The stable release includes AndroidX Security State version 1.1.0 and Security State Provider version 1.0.0. These libraries are designed for security-sensitive Android apps, including banking, fintech, healthcare…
Also in Malwarebytes Labs The Hacker News Bleeping Computer +3
-
An Undercover Google Analyst Infiltrated a Notorious Supply Chain Hacking Gang
TeamPCP pulled off the worst-ever software supply chain hacking spree and breached thousands of companies. Now Google’s threat intelligence group says it had a mole inside the hackers’ inner circle.
Also in CCCS Alerts & Advisories The Hacker News The Register Security +2

-
‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft
Executives working on AI at Microsoft and OpenAI admitted what its critics have been saying all along: Large language models are predatory pieces of technology that have been built on what a Microsoft executive called “an astonishing theft of unprecedented proportions,” and the “largest theft of labor in human history.” An internal Microsoft document said generative AI products have created a “doom loop” that is killing “the entire web.” Those statements and a series of other mask-off moments feature heavily in an unredacted court filing that was unsealed Thursday in the behemoth New York…
Also in Bleeping Computer Bleeping Computer Bleeping Computer +3
-
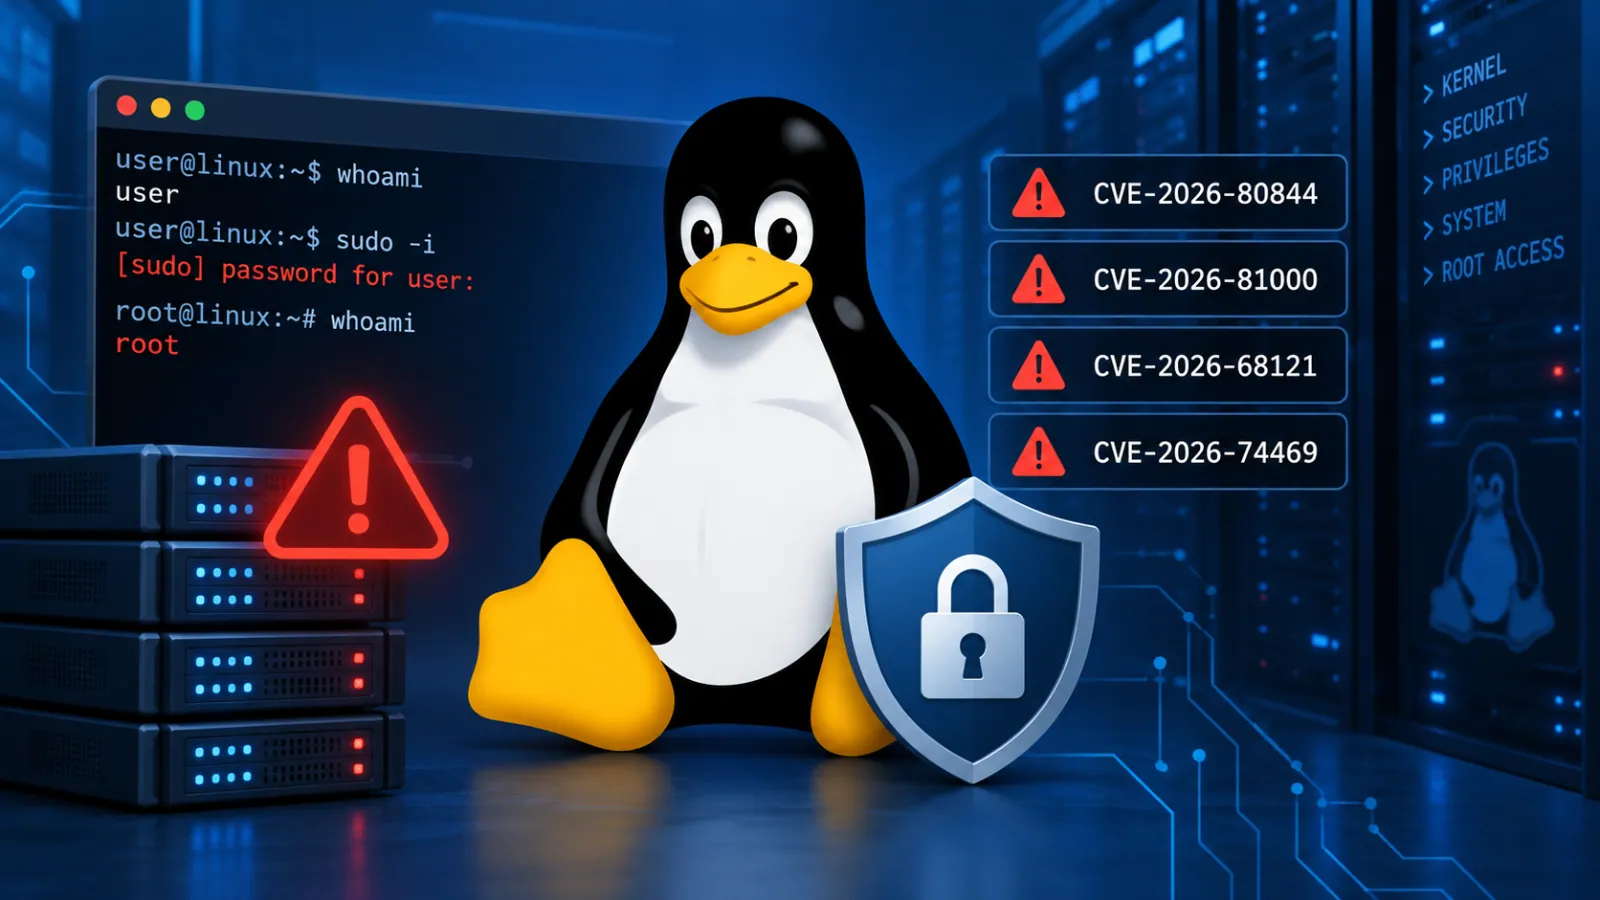
Linux Kernel Hit by Four Privilege Escalation Flaws Enabling Root Access
Four newly disclosed Linux kernel vulnerabilities could allow local attackers to corrupt kernel memory and escalate privileges to root on affected systems. The flaws, named DirtyAH6, TUNderflow, PPPoEject, and DiagSpill, affect long-standing networking code and have now received upstream fixes. The vulnerabilities are tracked as CVE-2026-80844, CVE-2026-81000, CVE-2026-68121, and CVE-2026-74469. DirtyAH6, tracked as CVE-2026-80844, affects IPv6 Authentication Header processing in Linux IPsec/XFRM code. The issue occurs when the kernel handles malformed IPv6 routing-header values without…
Also in CISA Alerts & Advisories Zero Day Initiative Dark Reading
-
Critical Microsoft Azure AI Foundry Vulnerability Allows Attackers to Escalate Privileges
Microsoft has patched a maximum-severity security flaw in Azure AI Foundry, its enterprise platform for building and managing generative AI applications and agents, that could have allowed an unauthenticated attacker to escalate privileges over the network without any user interaction. Tracked as CVE-2026-85889 , the vulnerability carries the highest possible CVSS score of 10.0, placing it among the most severe cloud security issues disclosed this year. According to Microsoft’s advisory, published on September 17, 2026, the root cause is a missing authentication check for a critical function…
Also in The Hacker News SecurityWeek Microsoft Security +2

-
Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point's Security Management and Log Servers could allow an attacker without login credentials to run code as root on those servers over the network. The Security Management Server is the system that controls firewall policy and administrator access. Check Point has released a fix through its LivePatch update channel and says it has no indication that the flaw
Also in Bleeping Computer SecurityWeek CCCS Alerts & Advisories

-
Cisco drops another exploited zero-day, this time a perfect 10
Cisco admins who have spent their week patching email gateways now face a perfect-10 Identity Services Engine flaw under active attack. Cisco disclosed CVE-2026-76460 on Wednesday, describing it as an authentication bypass affecting Identity Services Engine (ISE) and ISE Passive Identity Connector (ISE-PIC). Successful exploitation can give an unauthenticated remote attacker command execution with root privileges. Product Security Incident Response Team said it was aware of active exploitation and urged customers to install the fixes immediately. CISA has also added the vulnerability to its…
Also in CyberScoop CCCS Alerts & Advisories The Hacker News +1
-
Tutor LMS Flaw Exposes 100,000+ WordPress Sites to Remote Code Execution
A high-severity flaw in the Tutor LMS WordPress plugin could let a low-privileged user take control of an affected server. The issue affects more than 100,000 sites that use the e-learning plugin, particularly installations that allow visitors to register as students. Tracked as CVE-2026-78175, the vulnerability is rated 8.8 out of 10 and affects Tutor LMS versions 4.0.7 and earlier. An attacker needs a subscriber-level account, but on sites with open registration, creating that account may be as simple as completing a student sign-up form. Researchers noted that the bug can lead to remote…
Also in SecurityWeek Infosecurity Magazine The Hacker News

-
Inside the Modern SOC: Defending the Cross-Environment Pivot
Cross-environment attacks demand a new approach to security operations. Learn how Unit 42 Managed XSIAM helps SOC teams investigate complete attack paths.
Also in Cisco Security Advisories CISA Alerts & Advisories The Hacker News
-
New SETTRA Ransomware Uses MeshAgent RMM and BYOVD to Encrypt Windows Systems
Settra ransomware is emerging as a serious threat to Windows networks after investigators linked it to two recent intrusions involving remote-management software and recovery-blocking actions. The operation encrypts files, leaves victims with ransom notes, and tries to make both investigation and restoration more difficult. Public reporting indicates that the people behind Settra have gained entry through virtual private networks or previously stolen credentials. That makes exposed remote access and weak account controls a central concern, while the use of legitimate administration software…
Also in Sophos Threat Research The Register Security

Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-62104 | Migratico Litesuperweby | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isUnauthenticated Remote Code Execution (RCE) in Migratico Lite <= 2.6.8 versions. Attack
Exploitation
|
|||||||||
| CVE-2026-92937 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 3.11.6 is vulnerable to a sandbox escape leading to remote code execution in the host Node.js process. The fix for GHSA-m283-3h24-438v is incomplete: the bridge gate at lib/bridge.js:1624 identity-checks only the direct call target when… Attack
Exploitation
|
|||||||||
| CVE-2026-92940 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 versions 3.11.3 through 3.11.6 expose the host process's real https.globalAgent to sandboxed code when a NodeVM is explicitly configured to allow require('https'). The builtin loader wraps host modules in a read-only proxy, but method c… Attack
Exploitation
|
|||||||||
| CVE-2026-92941 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 versions from 3.11.3 before 3.11.7 expose the host tls module to NodeVM sandbox code, allowing attackers to call tls.setDefaultCACertificates() and replace process-wide certificate authorities. Attackers with access to allowed tls and u… Attack
Exploitation
|
|||||||||
| CVE-2026-92946 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 before 3.11.7 contains a remote code execution vulnerability when require.external is enabled without an explicit require.root that excludes node_modules. Sandboxed code can require vm2's own package, instantiate an unrestricted NodeVM … Attack
Exploitation
|
|||||||||
| CVE-2026-92947 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 before 3.11.7 exposes Node's shared Buffer pool to sandboxed code, allowing disclosure of host memory used by Buffer.from, Buffer.concat, and related allocations. Sandboxed code can read and write to host-realm buffers by acquiring Arra… Attack
Exploitation
|
|||||||||
| CVE-2026-92953 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 versions from 3.11.0 before 3.11.8 fail to protect host TypedArray and ArrayBuffer prototypes from sandbox mutation. Attackers can use prototype-walking primitives to reach and modify host Uint8Array.prototype, %TypedArray%.prototype, a… Attack
Exploitation
|
|||||||||
| CVE-2026-92955 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 before 3.11.8 contains a sandbox escape vulnerability in NodeVM that allows attackers to access the host __proto__ getter/setter through console._stdout and console._stderr. Attackers can overwrite EventEmitter.prototype.emit and trigge… Attack
Exploitation
|
|||||||||
| CVE-2026-92956 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 versions 3.10.1 through 3.11.6 contain a sandbox escape reachable from a default `new VM()` sandbox when running on Node.js 26. WebAssembly.compileStreaming and WebAssembly.instantiateStreaming can produce a raw host-realm Promise that … Attack
Exploitation
|
|||||||||
| CVE-2026-92960 | vm2patriksimek | Critical | 10.0 | — | — | — | — | CVSS 10.0 | |
What it isvm2 before 3.11.6 fails to restrict access to os and dns builtins under the builtin: ['*'] configuration, allowing sandbox code to read host process identity and network topology. Attackers can invoke dns.setServers() to hijack the host pro… Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Worth reading quieter, still worth your time
-
ZDI-26-718: Cisco Identity Services Engine MnTRESTLivelogService XML External Entity Processing Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Cisco Identity Services Engine. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 4.9. The following CVEs are assigned: CVE-2026-20235.
Also in Zero Day Initiative Zero Day Initiative CCCS Alerts & Advisories +1
-
Exploring the new AWS Sign Up experience
This post will explore what this new concept does, how it works with the new Account Access capability, and why a strong security posture still requires upgrading out of the sandbox.
Also in Palo Alto Unit 42
-
ZDI-26-703: (0Day) Airbyte SharePoint Connector _get_shared_drive_object Server-Side Request Forgery Information Disclosure Vulnerability
This vulnerability allows remote attackers to initiate arbitrary server-side requests on affected installations of Airbyte. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.7. The following CVEs are assigned: CVE-2026-92203.
Also in Microsoft Security
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.