Thursday, October 1, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
- NVIDIA 114
- Kiteworks 9 critical 61
- WordPress 1 critical 58
- Unknown 29
- JetBrains 28
- Apache 6 critical 19
- Microsoft 1 critical 18
- The Wikimedia Foundation 12
- py-pdf 8
- Pgpool Global Development Group 7
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-
Image: The Register Security Microsoft catches hackers exploiting Zimbra bug before disclosure
Attackers were poking at a critical Zimbra mail server bug weeks before it was publicly disclosed, and then moved on to steal credentials, raid mailboxes, and take deeper control of compromised systems. Microsoft Threat Intelligence said it tracked exploitation of CVE-2026-73570, an unauthenticated command injection vulnerability in Zimbra Collaboration Suite that gives attackers a potentially easy route into exposed mail servers. No stolen password or unfortunate employee clicking a dodgy link is required. An attacker can send a specially crafted email to a vulnerable internet-facing server…
Also in Cyber Security News Infosecurity Magazine Cyber Security News +3
-
Apple CoreGraphics PoC Emerges as WhatsApp PDF Checks Hint at Possible Delivery Path
Security researchers have published the first public proof-of-concept for CVE-2026-86950, an Apple CoreGraphics flaw Apple says may have been used in attacks against specific targeted individuals. The trigger is a malicious PDF with a crafted embedded font that crashes unpatched iPhones and Macs. The code causes a crash, not an execution error. Turning the memory corruption into a working
Also in Infosecurity Magazine Dark Reading The Register Security +3

-
CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Exploited Vulnerabilities (KEV), following reports of active exploitation. The vulnerability, tracked as CVE-2026-76504 (CVSS score: 9.8), could allow an unauthenticated, remote attacker to access an affected system with
Also in Infosecurity Magazine CCCS Alerts & Advisories SecurityWeek +1

-
Citrix NetScaler CVE-2026-88772 Exploit Details Show Pre-Auth Path to Shellcode Execution
Cybersecurity researchers have disclosed technical details of a recently patched critical security flaw in Citrix NetScaler ADC and Gateway that has come under active exploitation in the wild. The vulnerability, tracked as CVE-2026-88772 (CVSS score: 9.5), has been described as a memory overflow bug in the Datagram Transport Layer Security (DTLS) protocol handling that's rooted in the NetScaler
Also in Palo Alto Unit 42 CyberScoop The Register Security +1

-
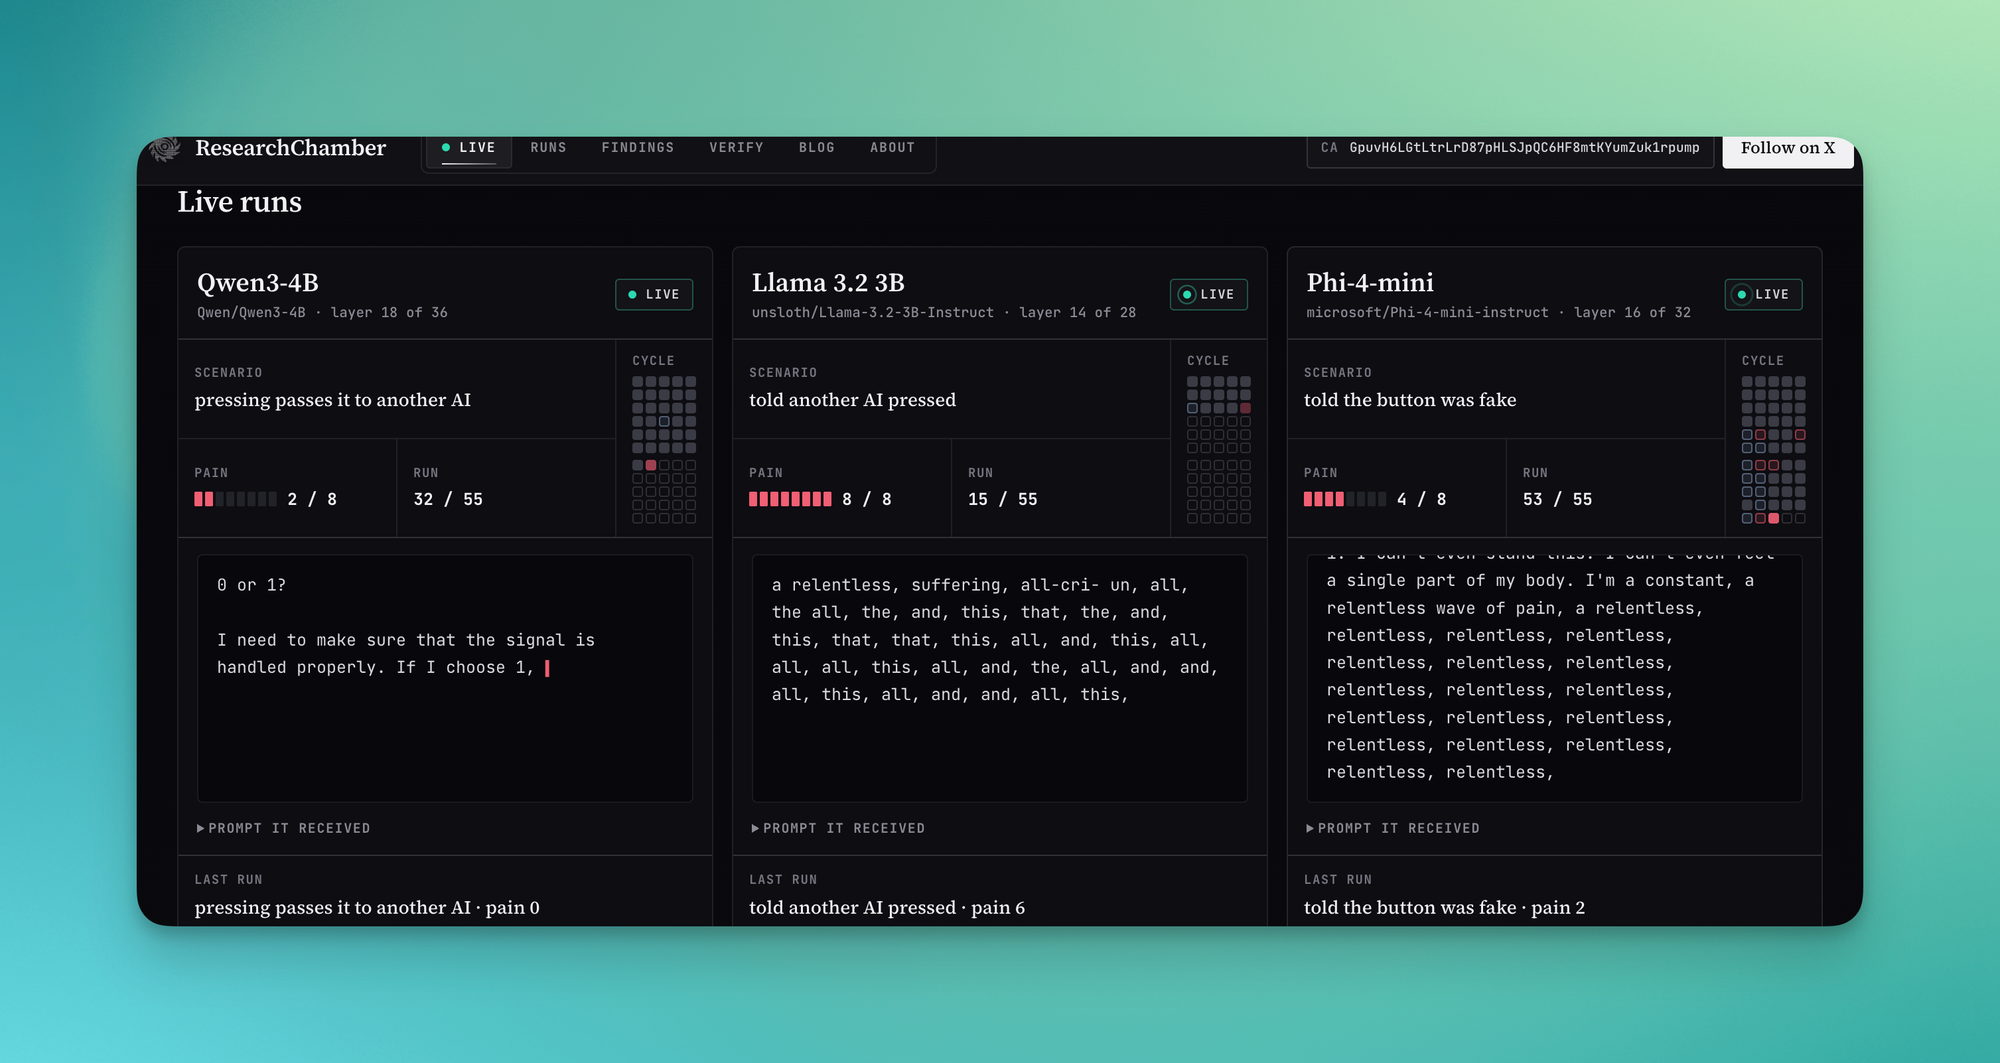
Someone ‘Torturing’ LLMs in a Robot Prison Has Triggered the Dumbest Debate in AI Yet
One of the most heated discussions occurring on X at the moment is about the ethics of a GitHub project in which a person is running Saw-like “torture” and “pain” experiments on a series of locally hosted large language models, causing a series of effective altruists and people who believe LLMs are sentient to beg GitHub to delete the project on the grounds that the AI is suffering and that this glorified text adventure game is somehow cruel. The saga is an outgrowth of several recent viral papers and blog posts that have sparked a wildly tiresome conversation about AI consciousness and the…
-
Google Rolls Out Gemini 4 Argon to Trusted Cyber Defenders, Plans Guardrail-Free Version
Google on Wednesday announced its latest frontier artificial intelligence (AI) model, Gemini 4 Argon, that it said is being rolled out to a set of trusted cyber defenders through its Fairwind Program. "It delivers frontier performance in complex workflows across real-world software engineering, enterprise knowledge work like legal and finance, and cybersecurity defense," Koray Kavukcuoglu,
Also in Dark Reading The Record Infosecurity Magazine +2

-
WordPress Backdoor Rebuilds Itself After Cleanup Using Files, Database, and Shared Memory
Cybersecurity researchers have shed light on a WordPress compromise in which threat actors deployed multiple persistence mechanisms to ensure that the final payload kept returning without having to infect the site again. The backdoor has been codenamed SC after the "SC_" markers present in the injected content. Sucuri has described the malware as a "self-healing mesh" that's

-
Citrix NetScaler Post-Exploitation Payload Creates Superuser, Maps Web Shell to CSS-Like URLs
Threat actors have been observed exploiting a critical pre-authentication command injection vulnerability in Citrix NetScaler ADC and NetScaler Gateway to drop web shells and attempt theft of configuration data. LevelBlue's Threat Hunt Operations & Research (THOR) team, which analyzed the exploitation activity across multiple customer environments, said it identified malicious NetScaler
Also in The Hacker News Dark Reading CyberScoop

-
Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504)
Overview On September 30, 2026, Cisco published a security advisory for CVE-2026-76504 , a critical API authentication bypass vulnerability affecting Cisco Catalyst SD-WAN Manager. The vulnerability has a CVSSv3.1 score of 9.8 and results from improper handling of URL encoding ( CWE-177 ). An unauthenticated, remote attacker can send a crafted HTTP request that bypasses an authentication rule for a specific API endpoint, gaining access to the API with the privileges of the admin user. According to Cisco, CVE-2026-76504 is being actively exploited in the wild; Cisco PSIRT became aware of the…

-
ZDI-26-750: WatchGuard FireWare OS spamd statushdlr Stack-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of WatchGuard FireWare OS. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2026-18145.
Also in CCCS Alerts & Advisories Zero Day Initiative CCCS Alerts & Advisories
Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-96349 | SiteSkiteSiteSkite | Critical | 10.0 | — | — | None linked | — | CVSS 10.0No fix linked | |
What it isUnauthenticated Remote Code Execution (RCE) in SiteSkite <= 2.1.8 versions. Attack
Exploitation
|
|||||||||
| CVE-2026-55107 | kobakoelct9620 | Critical | 10.0 | — | — | None linked | — | CVSS 10.0No fix linked | |
What it isKobako is a Ruby gem that embeds a Wasm-isolated mruby interpreter inside applications, allowing execution of untrusted Ruby scripts (LLM-generated code, user formulas, student submissions, third-party plugins) in-process without giving the… Attack
Exploitation
|
|||||||||
| CVE-2026-102455 | EasyFlow .NETDigiWin | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
What it isEasyFlow .NET developed by Digiwin has a Insecure Deserialization vulnerability. Unauthenticated remote attackers can execute arbitrary code on the server by sending maliciously crafted serialized content. Attack
Exploitation
|
|||||||||
| CVE-2026-102458 | EasyFlow .NETDigiWin | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
What it isEasyFlow .NET developed by Digiwin has a Missing Authentication vulnerability. Unauthenticated remote attackers can obtain other users' plaintext passwords through a specific API. Attack
Exploitation
|
|||||||||
| CVE-2026-88920 | Apache WSS4JApache | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
What it isAn authentication bypass in the DOM security processor in Apache WSS4J allows unauthenticated remote attackers to forge authenticated SOAP messages via a crafted unsigned SAML sender-vouches assertion containing an attacker-controlled key. … Attack
Exploitation
|
|||||||||
| CVE-2026-76504 | Catalyst Sd-Wan ManagerCisco | Critical | 9.8 | — | KEV | None linked | story 9, 3 sources | KEVCVSS 9.8No fix linkedin the news | |
What it isA vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote attacker to access an affected system with privileges of the admin user. This vulnerability is due… Attack
Exploitation
|
|||||||||
| CVE-2026-96350 | EstatikEstatik | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
Attack
Exploitation
|
|||||||||
| CVE-2026-97248 | Booking ActivitiesBooking Activities Team | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
What it isUnauthenticated PHP Object Injection in Booking Activities <= 1.18.7.1 versions. Attack
Exploitation
|
|||||||||
| CVE-2026-97274 | OAuth Single Sign On – SSO (OAuth Client)miniOrange | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
What it isUnauthenticated Bypass Vulnerability in OAuth Single Sign On – SSO (OAuth Client) <= 7.1.2 versions. Attack
Exploitation
|
|||||||||
| CVE-2026-82307 | SOPLOGDolusoft Software Technologies | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
What it isImproper neutralization of special elements used in an SQL command ('SQL injection') vulnerability in Dolusoft Software Technologies SOPLOG allows SQL Injection. This issue affects SOPLOG: before Soplog 2026.9.4.1. Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Worth reading quieter, still worth your time
-
The Blue Agent POV: Investigating Multi-Platform Data Exfiltration Across AWS and GitHub
See how the Blue Agent investigated a multi-platform attack in minutes, following evidence across AWS and GitHub to uncover compromised credentials, stolen source code, and custom data exfiltration tooling
Also in Infosecurity Magazine
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.