Tuesday, October 27, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
- Apple 326
- Unknown 2 critical 62
- WordPress 17
- Microsoft 1 critical 17
- Openpanel-dev 14
- Apache 12
- boneIO 11
- mtrudel 10
- HashiCorp 1 critical 9
- Linux 9
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-
Image: The Register Security Microsoft releases out-of-band Windows fixes with certificate updates
Microsoft has released another out-of-band update for Windows, but this one isn't an emergency fix for the latest breakages. This time, it's all about certificates. The non-security out-of-band release applies to supported OSes ranging from Windows 11 and Windows Server 2025, to Windows 10. It's all about updating the current certificate trust list (CTL) of devices that cannot access Microsoft's certificate-update service, or where automatic CTL updates are disabled. It also contains everything in the October 13 update, including the ongoing VPN issues and the change that could break…
Also in The Hacker News CyberScoop Huntress +3
-
PHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution Flaw
PHP has rebuilt its official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a flaw in the Brotli compression library that the packages include. The flaw can let an attacker corrupt memory and potentially run code. PHP says the flaw can be reached through the cURL extension when the extension decompresses HTTP responses automatically. cURL leaves that off by default, but
Also in Tenable Blog CyberScoop Rapid7 Blog +2

-
Apple iOS 27.2 Released With Fixes for 163 Vulnerabilities, Including Fix for Critical WebKit RCE
Apple released iOS 27.2 and iPadOS 27.2 on October 26, 2026, with fixes for 163 security flaws. The update covers iPhone 11 and later and a wide set of iPad models. The most serious issues sit in WebKit, the engine behind Safari and most in-app browsers on Apple devices. Apple says malicious web content could run code on a device. That is a remote code execution risk, and it is the reason this update should not wait. Apple published the full list in its security content document for iOS 27.2 and iPadOS 27.2 . The company does not report active use of these flaws in real attacks. That does not…
Also in SecurityWeek Bleeping Computer Cyber Security News +2

-
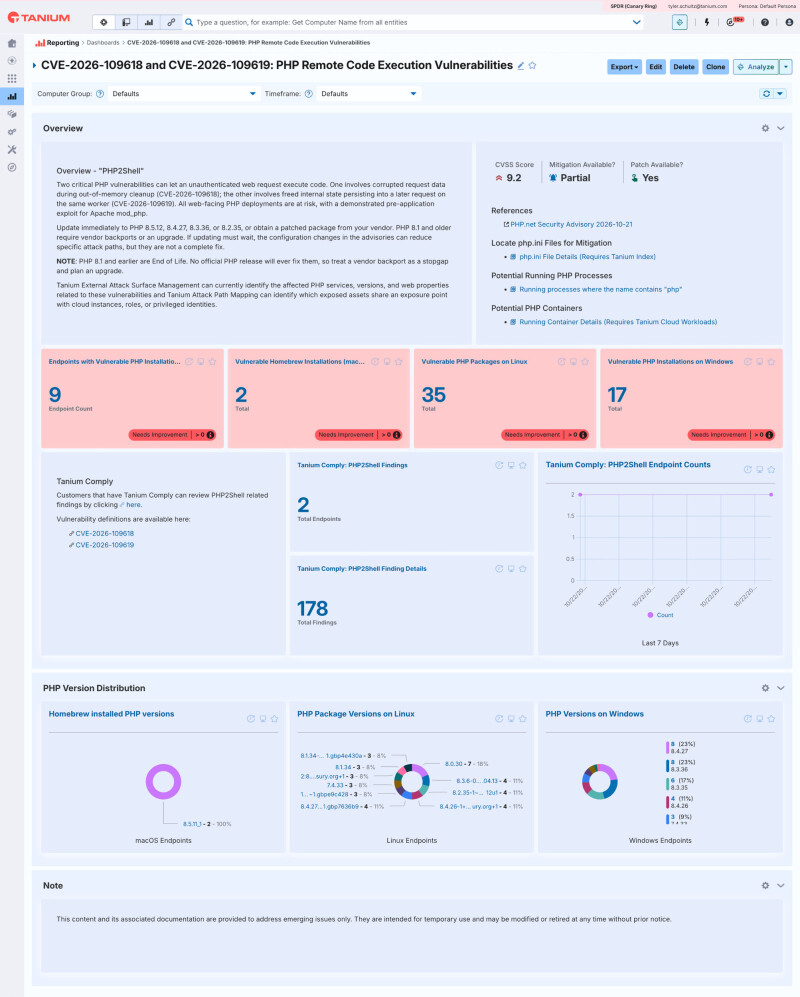
PHP2Shell: No login, no app code, no warning. What next?
If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed last week, CVE-2026-109618 and CVE-2026-109619 (nicknamed "PHP2Shell"), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported. The patch is the easy part. The hard part is finding every copy of PHP you own, because PHP rarely shows up where you expect it. This post covers what the flaws are, how far…
Also in Cisco Security Advisories Tenable Blog ESET WeLiveSecurity +2
-
Worm armed 42 GitHub repos by hiding a payload too big to fail
A new Miasma-family npm worm, originally believed to be just a test with no victims, secretly armed 42 real GitHub repositories from 11 owners, hijacking accounts as early as July and using a stealthy payload built to stay hidden from GitHub and automated scanners, according to JFrog researchers. Threat hunters at SafeDep, an open source supply chain security firm, first spotted the “testmetest” npm campaign last week, identifying 18 packages linked to the same operator between October 19 and October 25, including releases containing credential-stealing malware. As with earlier npm worms, the…
Also in The Register Security Dark Reading Infosecurity Magazine +3
-
Hackers Hijack AI Pentesting Agents to Install Backdoors and Steal API Keys
Hackers are now targeting the AI tools that security teams use to test their own networks. A new investigation describes automated campaigns that break into exposed panels for Cairn, a platform that gives AI agents goals and lets them work on their own. Once inside, the attackers push new tasks into those agents. These tasks install unauthorized SSH keys, download a remote access trojan, and search for stored API keys. The activity started on October 20, 2026, although some signs point to earlier probing. Cairn is built to make AI agents easy to run. A user defines a goal and a starting…
Also in Infosecurity Magazine

-
DreamHost Forces Email and FTP Password Resets Following Unexplained Security Incident
DreamHost forced password resets for affected email and FTP/SFTP accounts after an unexplained incident disrupted webmail and File Manager, preventing sign-ins until new credentials are set. DreamHost said the password resets were precautionary but has not disclosed the cause or confirmed data theft. The incident began on October 23, 2026, with File Manager connectivity issues. Later updates reported webmail errors and expanded the password resets to FTP/SFTP users. By October 26 at 3:35 p.m. PDT, engineers had restored the File Manager. They monitored the fix, but password changes remained…
Also in SecurityWeek

-
University of Copenhagen data breach exposes data of 525,000 people
The University of Copenhagen in Denmark confirmed that hackers accessed one of its test environments containing personal data belonging to 525,000 people.
Also in Infosecurity Magazine
-
Microsoft releases emergency .NET security fixes for Google Brotli bug
To address a vulnerability in Google's Brotli compression technology that could allow attackers to corrupt process memory, Microsoft is urging .NET users to update "as soon as possible" after releasing an out-of-band (OOB) security update. It released new versions for .NET 8, 9, 10, and .NET 11 to patch against the Brotli bug, following similar updates from Node.js, Python, and other projects. Senior program manager Rahul Bhandari said in the October 25 release that the buffer overflow vulnerability in Brotli, tracked as CVE-2026-111497 and rated 8.1 under CVSS v3.1 in Microsoft's advisory…
Also in CCCS Alerts & Advisories
-
Industrial Vendors Check Products for PHP2Shell Vulnerabilities
Siemens, Schneider Electric, ABB and others have confirmed that some of their products are affected by the PHP2Shell vulnerabilities.
Also in CCCS Alerts & Advisories
Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-116508 | A950RGTOTOLINK | Critical | 10.0 | — | — | None linked | — | CVSS 10.0No fix linked | |
What it isA security flaw has been discovered in TOTOLINK A950RG 4.1.2cu.5268_B20221104. Affected by this issue is the function sub_402340 of the file infostat.cgi of the component Device-Information CGI. Performing a manipulation of the argument CON… Attack
Exploitation
|
|||||||||
| CVE-2026-116231 | Pugongying X5 ProOray | Critical | 9.9 | 0.4% | — | None linked | — | EPSS 0.4%CVSS 9.9No fix linked | |
What it isA security flaw has been discovered in Oray Pugongying X5 Pro 7.6.1. The impacted element is an unknown function of the component Ser2net. Performing a manipulation of the argument regmsg results in crlf injection. It is possible to initiat… Attack
Exploitation
|
|||||||||
| CVE-2026-116232 | Pugongying X5 ProOray | Critical | 9.9 | 0.4% | — | None linked | — | EPSS 0.4%CVSS 9.9No fix linked | |
What it isA weakness has been identified in Oray Pugongying X5 Pro 7.6.1. This affects the function snmp_set of the component SNMP Handler. Executing a manipulation of the argument info.community can lead to crlf injection. It is possible to launch t… Attack
Exploitation
|
|||||||||
| CVE-2026-115188 | Unknown | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isAn unrestricted file upload vulnerability exists in the campaign import feature of Mautic 7. When processing an uploaded campaign archive, the application copies the bundled asset files into a publicly accessible media directory without res… Attack
Exploitation
|
|||||||||
| CVE-2026-102649 | burritoGitLab | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isBurrito is a Terraform Automation Collaboration Software (TACoS) Kubernetes operator. Prior to 0.13.0, `POST /api/webhook` accepts unsigned GitHub and GitLab events when a `TerraformRepository`'s credentials omit `webhookSecret` or set it t… Attack
Exploitation
|
|||||||||
| CVE-2026-110720 | ToolingHashiCorp | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isConsul-k8s versions 0.42.0 and later are vulnerable to a cross-namespace authorization bypass in component ACL binding rules that may allow an attacker to obtain elevated Consul privileges. This vulnerability (CVE-2026-110720) is fixed in c… Attack
Exploitation
|
|||||||||
| CVE-2026-116504 | A950RGTOTOLINK | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isA vulnerability has been found in TOTOLINK A950RG 4.1.2cu.5268_B20221104. This affects the function setCloudUpgradeFW of the file lib/cste_modules/upgrade.so of the component Cloud Upgrade. The manipulation of the argument FileName leads to… Attack
Exploitation
|
|||||||||
| CVE-2026-116506 | A950RGTOTOLINK | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isA vulnerability was determined in TOTOLINK A950RG 4.1.2cu.5268_B20221104. Affected is the function apmib_set of the file firewall.so. This manipulation causes command injection. The attack may be initiated remotely. The exploit has been pub… Attack
Exploitation
|
|||||||||
| CVE-2026-107092 | Unknown | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
What it isNexoPOS v6.2.4 is vulnerable to Directory Traversal via the api/update endpoint. Attack
Exploitation
|
|||||||||
| CVE-2026-107656 | FortiSandboxFortinet | Critical | 9.8 | — | — | None linked | — | CVSS 9.8No fix linked | |
What it isAn authentication bypass using an alternate path or channel vulnerability in Fortinet FortiSandbox 5.0.0 through 5.0.6, FortiSandbox 4.4.0 through 4.4.9, FortiSandbox 4.2 all versions, FortiSandbox PaaS 5.0.0 through 5.0.6, FortiSandbox Paa… Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.