Wednesday, October 28, 2026 · generated · about 5 min read
Morning Brief
Patch today vendors with the most new CVEs today
- Mozilla 174
- WordPress 4 critical 98
- Google 55
- Tanium 31
- SemanticMediaWiki 21
- Hitachi 18 critical 19
- WatchGuard 18
- Microsoft 1 critical 16
- asterisk 16
- redaxo 1 critical 15
Ranked by CVE count. Each vendor opens the CVE Feed filtered to that vendor and these dates.
Top developments ranked by cross-source trending
-

Image: Cyber Security News Hackers Compromise Camera Management Software to Deploy Malware on Windows Computers
Hackers have compromised camera management software to deploy malware on Windows computers, using a legitimate Microsoft program to run malicious code and maintain access. The activity shows how software used to manage surveillance systems can become an entry point into business networks. The incidents followed a similar pattern: attackers gained access through the camera application, deployed a suspected reverse shell, and used DLL sideloading to contact an outside server. Like earlier cases involving abuse of monitoring tools , the activity highlights risks surrounding software trusted for…
Also in Cyber Security News Bleeping Computer Bleeping Computer +3
-
PHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution Flaw
PHP has rebuilt its official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a flaw in the Brotli compression library that the packages include. The flaw can let an attacker corrupt memory and potentially run code. PHP says the flaw can be reached through the cURL extension when the extension decompresses HTTP responses automatically. cURL leaves that off by default, but
Also in CCCS Alerts & Advisories Tenable Blog CyberScoop +3

-
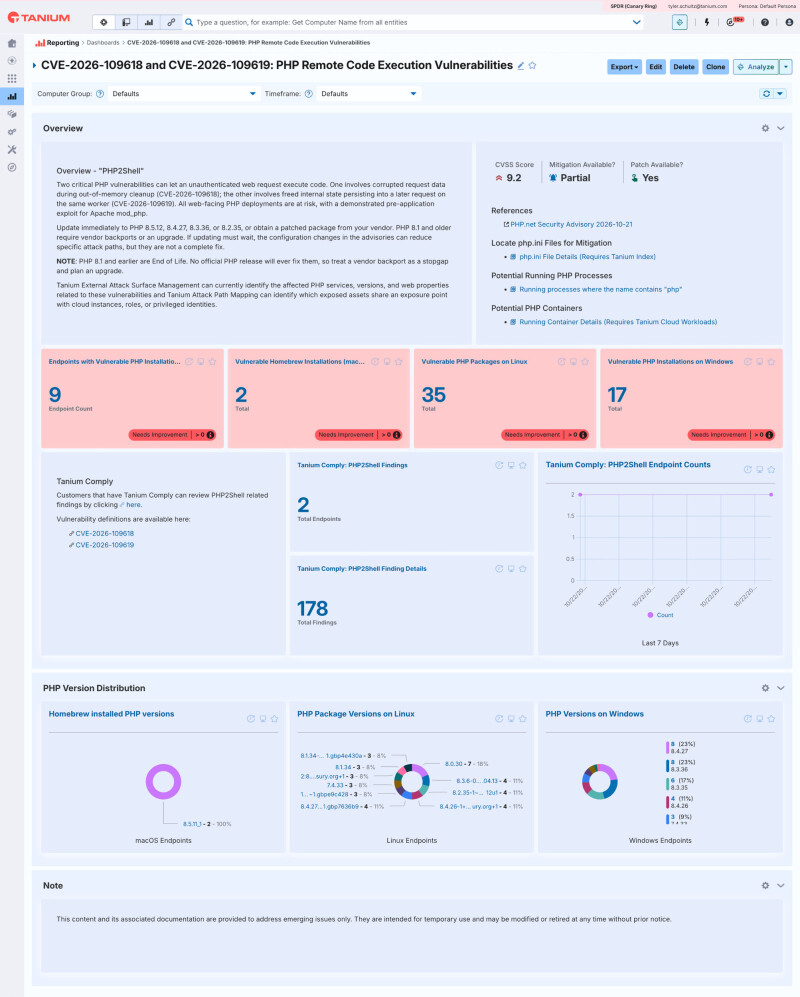
PHP2Shell: No login, no app code, no warning. What next?
If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed last week, CVE-2026-109618 and CVE-2026-109619 (nicknamed "PHP2Shell"), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported. The patch is the easy part. The hard part is finding every copy of PHP you own, because PHP rarely shows up where you expect it. This post covers what the flaws are, how far…
Also in Cisco Security Advisories CCCS Alerts & Advisories Tenable Blog +2
-
Worm armed 42 GitHub repos by hiding a payload too big to fail
A new Miasma-family npm worm, originally believed to be just a test with no victims, secretly armed 42 real GitHub repositories from 11 owners, hijacking accounts as early as July and using a stealthy payload built to stay hidden from GitHub and automated scanners, according to JFrog researchers. Threat hunters at SafeDep, an open source supply chain security firm, first spotted the “testmetest” npm campaign last week, identifying 18 packages linked to the same operator between October 19 and October 25, including releases containing credential-stealing malware. As with earlier npm worms, the…
Also in Check Point Research The Register Security Dark Reading +3
-
Hackers Actively Exploiting New Oracle EBS RCE Vulnerability
Hackers have begun testing a critical Oracle E-Business Suite vulnerability that can let them run commands without logging in. Threat intelligence firm Defused reported exploratory exploit attempts against its decoy systems on October 27, 2026. However, these observations do not confirm successful attacks against customer systems, and Oracle had already released a patch before the activity was detected. Tracked as CVE-2026-101767, the flaw carries a critical CVSS score of 9.8. Horizon3.ai discovered the issue and reported it to Oracle on July 24. Oracle fixed it on October 20 through its…

-
Anthropic's Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux Exploits
An unreleased Anthropic AI model found security flaws in Chrome, Safari, Android, Windows, and Linux and chained them into working proof-of-concept exploits, the company said in its latest report. The exploits were built in the lab after the model was prompted, not seen in any real attack, and Anthropic reported every flaw to the vendor first, so all of them are already patched. One proof of
Also in Malwarebytes Labs Google Project Zero

-
Cisco open sources tool for detecting AI agents on hacking sprees
Cisco has open sourced a behavior detection engine that watches AI agents, to help security teams prevent rogue agents from going off the rails like they did with the Hugging Face hack – or worse. It’s called Project Quarry, and it aims to provide a “shared language” for evaluating agent behavior, along the lines of what Snort, which Cisco also maintains, did for detecting malicious network traffic and what YARA did for rule-based malware identification. Most detection tools rely on specific interactions with an AI model or agent. Did it attempt prompt injection? Or did the agent call an…
-
Adobe Fixes 8 Critical Campaign Classic Flaws Allowing Code Execution and Security Bypass
Adobe has released patches to address multiple critical security flaws in Campaign Classic that, if successfully exploited, could result in arbitrary code execution, security feature bypass, and privilege escalation. The list of eight vulnerabilities is as follows - CVE-2026-104351 (CVSS score: 9.9) - A code injection vulnerability that could lead to arbitrary code execution.
Also in The Hacker News CCCS Alerts & Advisories CISA Alerts & Advisories

-
Apple Backports Fix for Exploited CoreGraphics Flaw to Older iPhones and iPads
Apple on Monday backported fixes for a high-severity security flaw that was exploited in real-world cyber attacks to older devices. The vulnerability, tracked as CVE-2026-86950 (CVSS score: 8.8), is an out-of-bounds write affecting CoreGraphics that could result in arbitrary code execution when processing a maliciously crafted file. Patches for the flaw were released last month by Apple in
Also in Bleeping Computer SANS Internet Storm Center 404 Media

-
Nefilim and Hive ransomware affiliate gets 70 months in prison
A Ukrainian national was sentenced to 70 months in prison for his role in ransomware attacks targeting hospitals, government entities, and high-revenue businesses worldwide between 2018 and 2021.
Also in CyberScoop
Vulnerability watch what to look at, most urgent first
| Details | CVE | Product | Severity | CVSS | EPSS | KEV | Fix | In the news | |
|---|---|---|---|---|---|---|---|---|---|
| Highest scoring today 10new CVEs, highest CVSS first | |||||||||
| CVE-2026-65145 | NeMo Agent ToolkitNVIDIA | Critical | 10.0 | — | — | None linked | — | CVSS 10.0No fix linked | |
What it isNVIDIA NeMo Agent Toolkit contains a vulnerability where a attacker could cause a missing authentication issue. This vulnerability might lead to code execution, escalation of privileges, data tampering, denial of service, and information di… Attack
Exploitation
|
|||||||||
| CVE-2026-105781 | Adobe Campaign ClassicAdobe | Critical | 10.0 | — | — | None linked | — | CVSS 10.0No fix linked | |
What it isAdobe Campaign Classic (ACC) is affected by an Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability that could result in arbitrary code execution in the context of the current user. An attacker … Attack
Exploitation
|
|||||||||
| CVE-2026-104351 | Adobe Campaign ClassicAdobe | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isAdobe Campaign Classic (ACC) is affected by an Improper Control of Generation of Code ('Code Injection') vulnerability that could result in arbitrary code execution in the context of the current user. A low-privileged attacker could exploit… Attack
Exploitation
|
|||||||||
| CVE-2026-104353 | Adobe Campaign ClassicAdobe | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isAdobe Campaign Classic (ACC) is affected by an Improper Neutralization of Special Elements used in an OS Command ('OS Command Injection') vulnerability that could result in arbitrary code execution in the context of the current user. A low-… Attack
Exploitation
|
|||||||||
| CVE-2026-105489 | Adobe Campaign ClassicAdobe | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isAdobe Campaign Classic (ACC) is affected by an Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability that could result in arbitrary code execution in the context of the current user. A low-privil… Attack
Exploitation
|
|||||||||
| CVE-2026-105780 | Adobe Campaign ClassicAdobe | Critical | 9.9 | — | — | None linked | — | CVSS 9.9No fix linked | |
What it isAdobe Campaign Classic (ACC) is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in the context of the current user. A low-privileged attacker could exploit this vulnerability to execute arb… Attack
Exploitation
|
|||||||||
| CVE-2026-18450 | X12SPISMCI | Critical | 9.8 | 0.4% | — | None linked | — | EPSS 0.4%CVSS 9.8No fix linked | |
What it isThe BMC does not correctly enforce integrity and encryption requirements for IPMI commands. An attacker may be able to craft packets that execute arbitrary commands on an active session. Attack
Exploitation
|
|||||||||
| CVE-2026-92885 | Qode MembershipWordPress | Critical | 9.8 | 0.4% | — | None linked | — | EPSS 0.4%CVSS 9.8No fix linked | |
What it isThe Qode Membership plugin for WordPress is vulnerable to Authentication Bypass leading to Account Takeover in all versions up to, and including, 2.0.6.2 via the qode_membership_check_facebook_user AJAX action. This is due to a typographic … Attack
Exploitation
|
|||||||||
| CVE-2026-76934 | JP1/Automatic Job Management System 3 - ManagerHitachi | Critical | 9.8 | 0.5% | — | None linked | — | EPSS 0.5%CVSS 9.8No fix linked | |
What it isStack-based Buffer Overflow Vulnerability in JP1/Automatic Job Management System 3. This issue affects JP1/Automatic Job Management System 3 - Manager: from 11-00 before 13-50-31; JP1/Automatic Job Management System 3 - Agent: from 11-00 b… Attack
Exploitation
|
|||||||||
| CVE-2026-76938 | JP1/Automatic Job Management System 3 - ManagerHitachi | Critical | 9.8 | 0.6% | — | None linked | — | EPSS 0.6%CVSS 9.8No fix linked | |
What it isAuthentication Bypass Vulnerability in JP1/Automatic Job Management System 3. This issue affects JP1/Automatic Job Management System 3 - Manager: from 10-00 before 13-50-31. Attack
Exploitation
|
|||||||||
Click a row, or press +, to expand it.EPSS is FIRST's estimated chance of exploitation in the next 30 days.Full CVE Feed
Assembled automatically, once a day, from data the Security Feed and CVE Feed already collect and score. No AI writes any of this, and every number traces back to something already published on those two tools.
Top developments come from the Security Feed's cross-source trending detection. Vulnerability watch comes from the CVE Feed's daily NVD and CISA KEV sync.